Dream Research · October 26, 2026
Chained PHP2Shell Exploit Roots 25 Servers, including US Government Servers
Custom PHP2Shell Exploit Chained with Kernel LPE to Root Firewalls in the Wild
On October 25, Dream researchers uncovered artifacts of what appeared to be a Chinese AI-assisted campaign that rooted 25 servers, including systems in a US government-affiliated environment. The attacker combined PHP2Shell with a kernel privilege-escalation exploit to compromise exposed systems.
The affected devices run specific versions of a large vendor’s firewall software. For security purposes, we are not disclosing the vendor or the affected versions, and the vendor has been notified.
The attacker then launched attacks against Active Directory. The recovered artifacts confirm credential extraction and directory enumeration.
The operation illustrates how an exposed management interface can become a path into an organization’s identity infrastructure. For government defenders, vulnerability discovery is just the beginning, after which the real challenge extends from identifying vulnerable systems to understanding and containing the access a compromise makes possible.
The research below was conducted with proactive threat hunting using Dream’s autonomous cyber research product, Hero*.*
Discovery
Dream researchers identified a complete attack operation that included a custom weaponization of the PHP2Shell exploit chain (CVE-2026-109618/CVE-2026-109619) paired with the Fragnesia kernel privilege escalation (CVE-2026-46300), target lists, exploitation logs, and approximately 40 custom post-exploitation scripts.
This included artifacts of a campaign that had rooted 25 servers across the United States, Japan, Taiwan, and South Korea. Once rooted, the attacker zeroed in on three specific servers in a US government-affiliated environment.
The discovered artifacts revealed an operation that began with exploit development in a lab environment and ended with persistent access to a US government organization's internal Active Directory domain.
AI Usage in Attack
We also observed some evidence of AI-assisted tooling in the attack infrastructure:
- Claude Code had been installed
- An AI-powered offensive security platform called aiscan was configured with Chinese LLMs DeepSeek and Kimi
- API keys for the Chinese reconnaissance platform FOFA were present
While we have no direct evidence that the AI tools were specifically used to write the exploit or the post-exploitation scripts, the code structure, commenting style, and consistency across ~40 scripts suggest AI-assisted development. That said, this operation does not appear to be a fully autonomous nation-state attack.
The Exploit: Two Vulnerabilities Chained Into One Request
The attacker developed two separate exploits and chained them together to achieve root access on any firewall running specific versions of a large vendor’s firewall software in a single HTTP request without any credentials.
PHP2Shell (CVE-2026-109618 / CVE-2026-109619) — Remote Code Execution
The implementation we recovered is a custom, non-public build, not a copy of any known public exploit for PHP2Shell. It follows the same underlying concept but appears to have been independently developed and tailored specifically for the targeted firewall platform.
The vulnerability targets PHP's session.upload_progress mechanism on the firewall's appweb management server. The firewall OS uses PHP 8.0.30 with a high memory limit that enables the memory corruption stages of the attack.
The attack works in four orchestrated stages:
- A1 — Memory Exhaustion (~383MB): The attacker floods the server with crafted multipart POST requests, each containing massive filenames and session progress data. This pushes PHP's memory allocator to its limits, forcing the system into a predictable memory layout.
- B1 — Information Leak: A second request forges the stale session ID length from A1, forcing an out-of-bounds read. The server's
Set-Cookieresponse header carries the leaked pointer value — giving the attacker the base address oflibphp.soin the running process. - A2 — Stale Reference Setup (~500MB): Another round of memory pressure initializes a session, leaving
http_session_varsas a livezend_reference, then triggers a second OOM that leavesmod_data=NULL— creating a stale reference the attacker can forge in B2. - B2 — Code Execution: The final request forges a PHP HashTable entry in the freed memory region. The forged entry's
pDestructorcallback points tozif_system(PHP'ssystem()function), and its data points to a shell command string. When PHP's cleanup handler walks the HashTable, it calls the forged destructor — executing arbitrary commands as thenobodyuser.
Fragnesia (CVE-2026-46300) — Kernel Privilege Escalation
Getting code execution as nobody isn't enough since SELinux confines httpd_t from modifying system files. In order to complete the root, the attacker chained in a second exploit: a Linux kernel vulnerability in the XFRM ESP-in-TCP subsystem.
Fragnesia uses page-cache writes to overwrite /etc/pam.d/su — replacing its authentication rules with pam_permit.so (accept all). Because the PAM file is only 774 bytes, the exploit uses a per-byte splicing variant to write it precisely. After the overwrite, su root succeeds without a password.
Both exploits run in a single B2 HTTP request. The total chain — from unauthenticated HTTPS connection to persistent root webshell — completes in under 15 minutes.
The Lab: Version Profiling at Scale
The exploit is not a single fire-and-forget payload. It requires precise memory offsets that differ between firewall OS versions — the address of zval_ptr_dtor, the address of zif_system, HashTable structure sizes, and memory geometry parameters that control the heap layout during each stage.
Among the recovered artifacts, we found 11 JSON version profile files — one for each firewall OS version that had been tested:
| Firewall Version | Release branch | PHP | Profiles | Notes |
|---|---|---|---|---|
| Redacted | Older branch | 7.4.33 | 2 provisional | PHP 7.4 — RCE as nobody verified in lab, but full chain not calibrated (base build plus one hotfix variant) |
| Redacted | Newer branches | 8.0.30 | 1 calibrated, 8 provisional | One base profile fully lab-tested; the others inherit its geometry or share offsets with neighboring builds |
Each profile contains the exact offsets extracted from the libphp.so binary of that version — with SHA256 hashes of each library, ELF build IDs, and precise memory geometry parameters (chunk sizes, fill counts, drain counts, spray offsets) tuned through lab testing.
The difference between "calibrated" and "provisional" profiles is notable — calibrated means the attacker tested the exploit against a running VM of that version and confirmed the memory geometry works. Provisional means they calculated offsets from the binary but haven't verified on a live instance.
The Campaign Funnel: From 19,000 Discovered to 25 Exploited
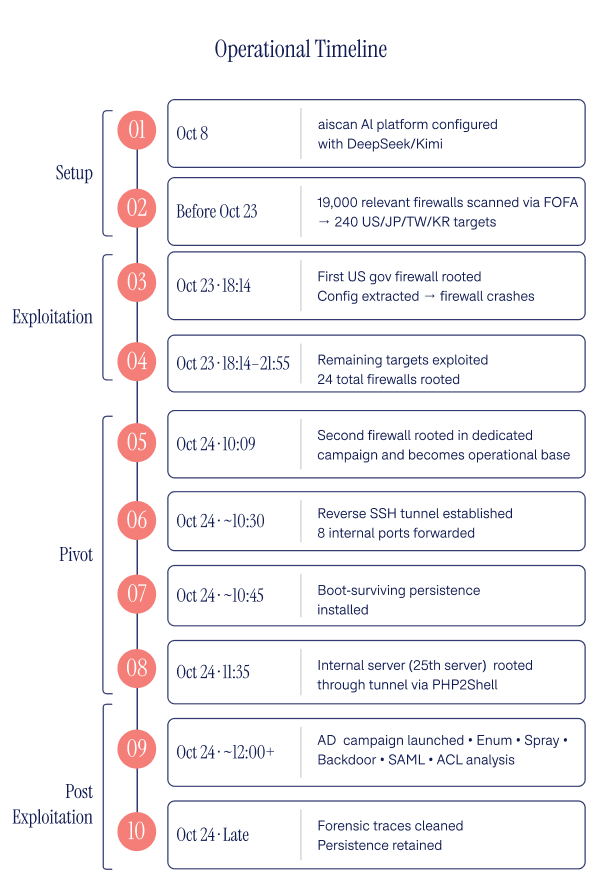
Figure 1: Operational timeline of the campaign, from setup on October 8 through exploitation, the pivot into the internal network, and post-exploitation on October 24.
With the exploit ready and profiles for 9 exploitable versions, the attacker launched a targeting campaign that followed a clear funnel:
Stage 1: Global Discovery (19,000 targets)
Using FOFA — a Chinese internet asset search engine similar to Shodan — the attacker identified approximately 19,000 internet-facing firewalls from the targeted vendor worldwide. These were devices with management interfaces exposed to the internet, discoverable through certificate fingerprints and HTTP response signatures.
Stage 2: Version Fingerprinting (5,000 alive)
A custom version scanner ran with 200 concurrent threads against all 19,000 targets, identifying which devices were actually online and what OS version they were running. Approximately 5,000 responded with version information.
Stage 3: Geographic and Version Filtering (240 targets)
From the 5,000 alive devices, the attacker filtered to servers located in only United States, Japan, Taiwan, and South Korea. They then further filtered to versions matching their exploit profiles (the newer release branches running PHP 8.0.30). This produced a final target list of 240 firewalls.
Since US, Japan, Taiwan, and South Korea are the four primary strategic adversaries and intelligence targets for Chinese state-aligned cyber operations in the Pacific theater, this indicates potential nation-state adversary efforts.
Stage 4: Automated Exploitation (24 rooted)
The 240 targets were fed into an automated batch runner that exploited them five at a time, with an 1800-second (30-minute) timeout per target. For each success, the batch:
- Ran the full PHP2Shell + Fragnesia chain
- Planted a 103-byte PHP root webshell in a publicly accessible directory on the firewall
- Verified root by executing
idthrough the webshell - Logged the target's hostname and IP to a success CSV
- Moved to the next target
At this point, 24 firewalls had been successfully rooted.
Stage 5: Triage (2 firewalls prioritized)
For 22 of the 24 rooted firewalls, the attacker did nothing beyond planting the webshell. No persistence, no tunnels, no post-exploitation tools. The servers were effectively owned and parked, allowing the attacker to return through the webshell at any time.
Two servers seemingly associated with one target progressed beyond this stage. Both appeared to belong to a US government-affiliated environment.
Stage 6: The Pivot (Shifting from Firewall to Domain)
Among the 24 rooted firewalls, two belonged to a US government-affiliated organization. The running configuration extracted from the first firewall revealed an environment with characteristics suggesting government affiliation: CAC (Common Access Card) authentication, a specific naming prefix, and standardized government-style asset naming. The configuration file contained the organization's complete internal network topology: domain controllers, a central firewall management server, a Keycloak SSO server, a GitLab instance, VPN gateways, and the Active Directory domain.
The first firewall was rooted on Oct 23 at 18:14 UTC during the automated batch. But it crashed shortly after — likely from the ~900MB of exploit traffic — and never came back online. The attacker monitored it with 240 automated probes over two hours, waiting for it to recover. It didn't. The second firewall, whose certificate data definitively linked it to the target organization, had timed out during the original batch.
Recognizing the organization's value from the first firewall's configuration, the attacker created a separate, dedicated campaign and successfully exploited it on Oct 24 at 10:09 UTC.
Within hours, the attacker:
Built a persistent tunnel into the internal network.
An 8-port reverse SSH tunnel connected the compromised firewall back to the operator's infrastructure, forwarding access to:
- Domain controllers (LDAP, LDAPS, RDP)
- The internal firewall management server
- VPN infrastructure
- A SOCKS5 proxy for arbitrary internal network access
The tunnel was wrapped in a systemd service and an rc.local boot hook — it survives reboots and automatically reconnects.
Exploited the management server through the tunnel. At 11:35 UTC, less than 90 minutes after rooting the second firewall, the attacker used the newly gained server access and the same PHP2Shell + Fragnesia chain against a third government server - the internal firewall management server that was only reachable through the tunnel. This server centrally manages all of the organization's firewalls. Compromising it gave the attacker access to every managed firewall's configuration, credentials, and network settings. This brought the total number of servers exploited to 25.
Launched an AD attack campaign from the management server. Because the management server already had LDAP connectivity to Active Directory (it needs it to authenticate VPN users), the attacker used it as their launch platform for domain attacks:
- Decrypted the LDAP service account password — the device config stores it encrypted, but with root access the attacker has the master key. They extracted it in plaintext and hardcoded it into every subsequent script.
- Enumerated every user and group in the domain via LDAP queries.
- Sprayed passwords against every user account using organization-themed passwords. The domain had
lockoutThreshold=0— meaning no account lockout, allowing unlimited spray attempts. - Attempted to create backdoor AD accounts — both a user account (tried in every OU) and a machine account (exploiting the default
MachineAccountQuotasetting). - Analyzed AD ACL chains for privilege escalation paths.
- Attempted SAML signing key extraction from the Keycloak IdP configuration.
- Probed Keycloak SSO for authentication bypass.
The attack results — whether the password spray found valid credentials, whether the backdoor accounts were created, whether SAML keys were extracted — stayed on the management server's local filesystem and were not among the artifacts we recovered. This means we cannot determine the full extent of the compromise.
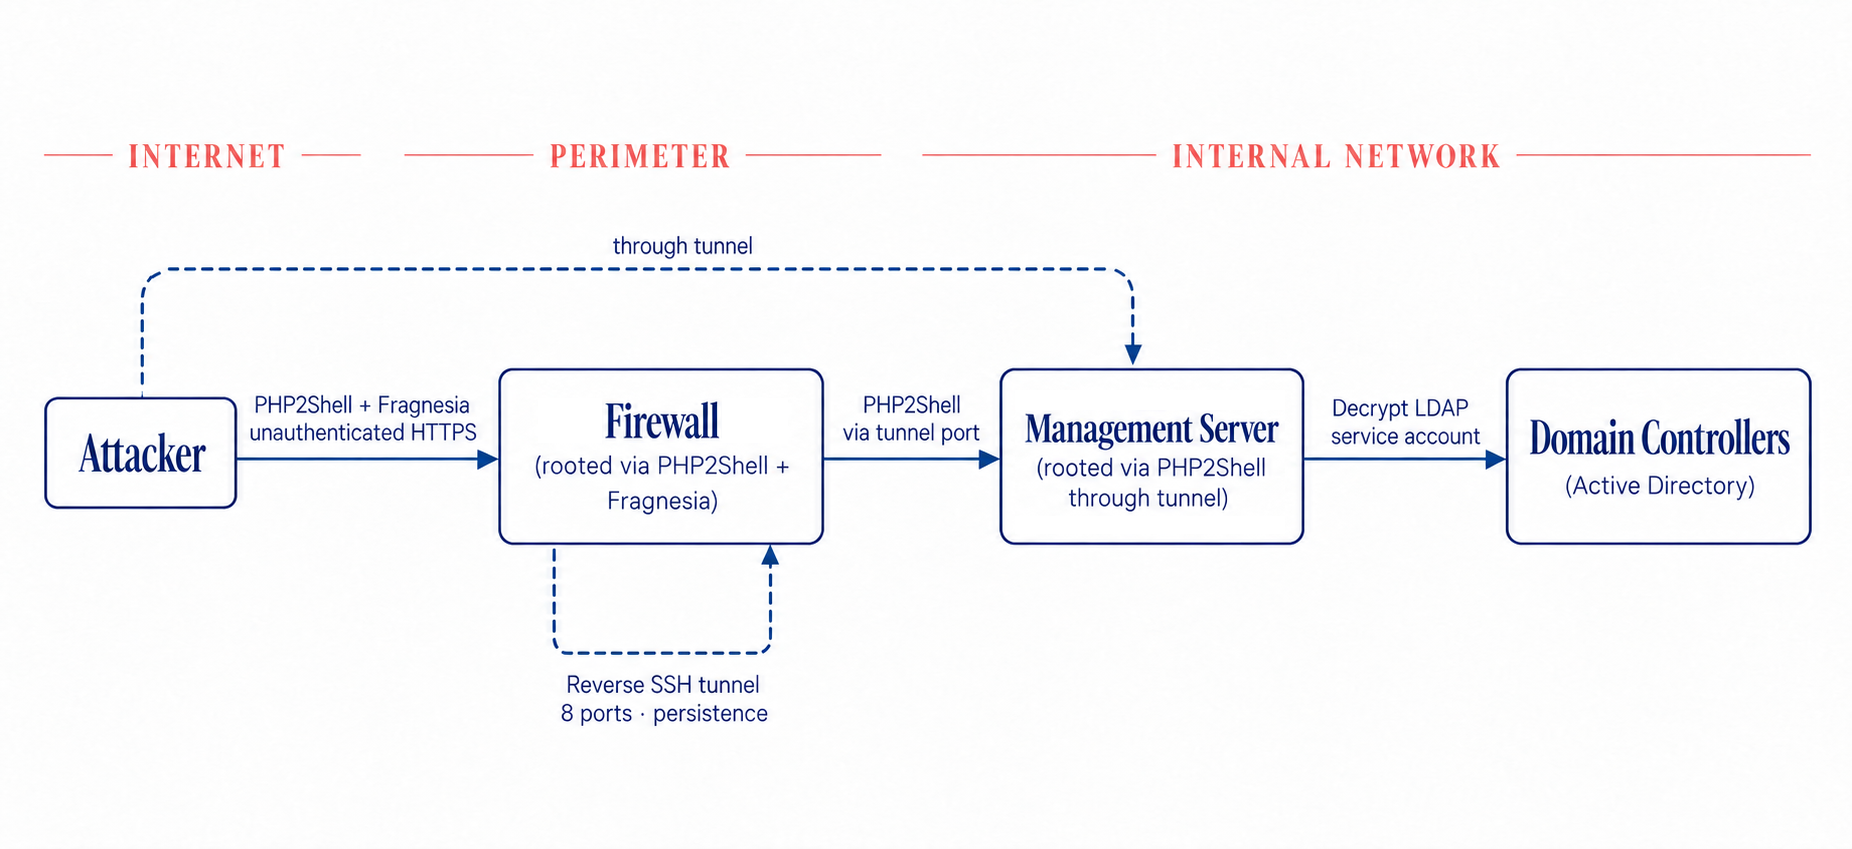
Figure 2: The attack path. PHP2Shell and Fragnesia root the perimeter firewall, a reverse SSH tunnel reaches the internal management server, and the decrypted LDAP service account opens Active Directory.
Management Server → Active Directory
| Status | Activity |
|---|---|
| ✓ | LDAP password decrypted from config |
| ✓ | Full user & group enumeration |
| ? | Password spray (all users, no lockout) |
| ? | Backdoor user + machine account creation |
| ? | SAML signing key extraction |
What the Attacker Has Now
From the recovered artifacts, we can confirm the attacker possesses:
- Persistent remote access to the organization's internal network via a boot-surviving reverse tunnel and SOCKS proxy — likely still active
- Root webshells on two firewalls and the firewall management server — likely still active
- The full Active Directory user and group listing — a complete organizational blueprint
- Decrypted LDAP service account credentials — enabling direct AD queries at any time
- Private keys harvested from the firewall filesystem — HA replication keys, SSL/TLS certificate keys, and device authentication keys
- Complete network topology — every IP, hostname, subnet, server role, and VPN gateway
- SAML IdP configuration with weak security settings (
validate-idp-certificate: no) - 22 additional parked firewalls across the US, Japan, Taiwan, and South Korea — ready for exploitation at any time
What we cannot determine is whether the password spray, backdoor account creation, or SAML key extraction succeeded. If any of these attacks worked, the compromise extends far beyond the perimeter firewalls into the organization's identity infrastructure.
Attribution Indicators
We do not attribute this activity to a named threat actor. However, multiple indicators point to a Chinese-nexus operation:
| Indicator | Detail |
|---|---|
| Target selection | US, Japan, Taiwan, South Korea exclusively. These are the primary strategic intelligence targets for Chinese state-aligned operations in the Pacific. |
| FOFA | The internet reconnaissance platform used to discover targets is a Chinese service. |
| iox | A Chinese-developed tunneling utility observed among the recovered tools. |
| DeepSeek and Kimi | The LLMs configured in the aiscan offensive security platform are Chinese language models. |
| UTC+8 timestamps | The infrastructure's clock ran on China Standard Time, confirmed by comparing log timestamps against HTTP Date: response headers from targets. |
| Chinese-language prompts | The aiscan session logs contain user messages in Chinese. |
Conclusion
This operation demonstrates a level of preparation and capability that sets it apart from opportunistic exploitation. The attacker invested significant effort into vulnerability research — obtaining the vendor’s firmware, decrypting it, extracting PHP libraries, building precise memory profiles for 9 different software versions, and calibrating exploit geometry through lab testing. The exploitation itself was automated and efficient: 240 targets attempted in a single batch, with version-specific profiles selected automatically.
There was a clear-cut focus on government targets.
The attacker scanned 19,000 firewalls, rooted 24, and immediately identified the two that mattered. Within hours of compromising a US government-affiliated firewall, they had tunneled into the internal network, compromised a third server using the same PHP2Shell exploit, and launched a full Active Directory attack campaign — all through a chain that started with a single unauthenticated HTTPS request to a management interface that should never have been exposed to the internet.
The 22 other rooted firewalls remain parked with active webshells. The persistent tunnel into the US government organization is likely still running. And the attacker still has 19,000 fingerprinted targets they can revisit as they develop profiles for additional OS versions.
As always, we recommend that organizations rapidly deploy relevant patches. Follow your vendor’s guidance for more information on this issue.
Closing the Gap Between Discovery and Defense
For governments and critical infrastructure, finding a vulnerability is only the beginning. Defenders need to identify exposed systems, establish what attackers can exploit, and act before a foothold becomes a wider compromise.
Dream addresses that challenge through two complementary cyberdefense platforms:
- Sphere scales national cyber defense. It maps exposure, prioritizes risks, and detects and responds to attacks across government networks, tailored to each nation’s threats and infrastructure.
- Hero scales cyber research. Its autonomous research agents help experts investigate threats, discover and validate vulnerabilities—including in software without source code—and develop remediation guidance and patches. This is the tool that was used by Dream researchers to conduct the investigation detailed in this post.
Together, they connect deeper investigation with defense across the national attack surface.
Originally published at Dream.