Research · Security, Open Source, Linux

*sshole

First published at sshhole.com.

Wakefield researcher Ozgun Kultekin details a decade-old OpenSSH bug on musl Linux (Alpine and others) where passwordless accounts accept any password over 256 characters, fixed in OpenSSH 10.6p2.

*ss h ole

so openssh on musl linux (alpine, openwrt, buildroot, yocto, and a lot of the docker images you've pulled) has had a little problem since 2016.

accounts that should never take a password at all (root, your key-only deploy user, ldap users, the default user on alpine's aws and azure images) take any password longer than 256 characters.

yes, any password.yes.i know.yes.

  1. 1980 the first star
  2. 1990s the password check
  3. 1990s the fine print
  4. 2012 crypt stops saying NULL
  5. 2012 the 256-byte cap
  6. 2016 bob's salt
  7. 2019 the fix for the fix
  8. 2024 ten quiet years
  9. 2026 how i ran into it

Research · Security, Open Source, Linux

*sshole

First published at sshhole.com.

Wakefield researcher Ozgun Kultekin details a decade-old OpenSSH bug on musl Linux (Alpine and others) where passwordless accounts accept any password over 256 characters, fixed in OpenSSH 10.6p2.

*ss h ole

so openssh on musl linux (alpine, openwrt, buildroot, yocto, and a lot of the docker images you've pulled) has had a little problem since 2016.

accounts that should never take a password at all (root, your key-only deploy user, ldap users, the default user on alpine's aws and azure images) take any password longer than 256 characters.

yes, any password.yes.i know.yes.

  1. 1980 the first star
  2. 1990s the password check
  3. 1990s the fine print
  4. 2012 crypt stops saying NULL
  5. 2012 the 256-byte cap
  6. 2016 bob's salt
  7. 2019 the fix for the fix
  8. 2024 ten quiet years
  9. 2026 how i ran into it
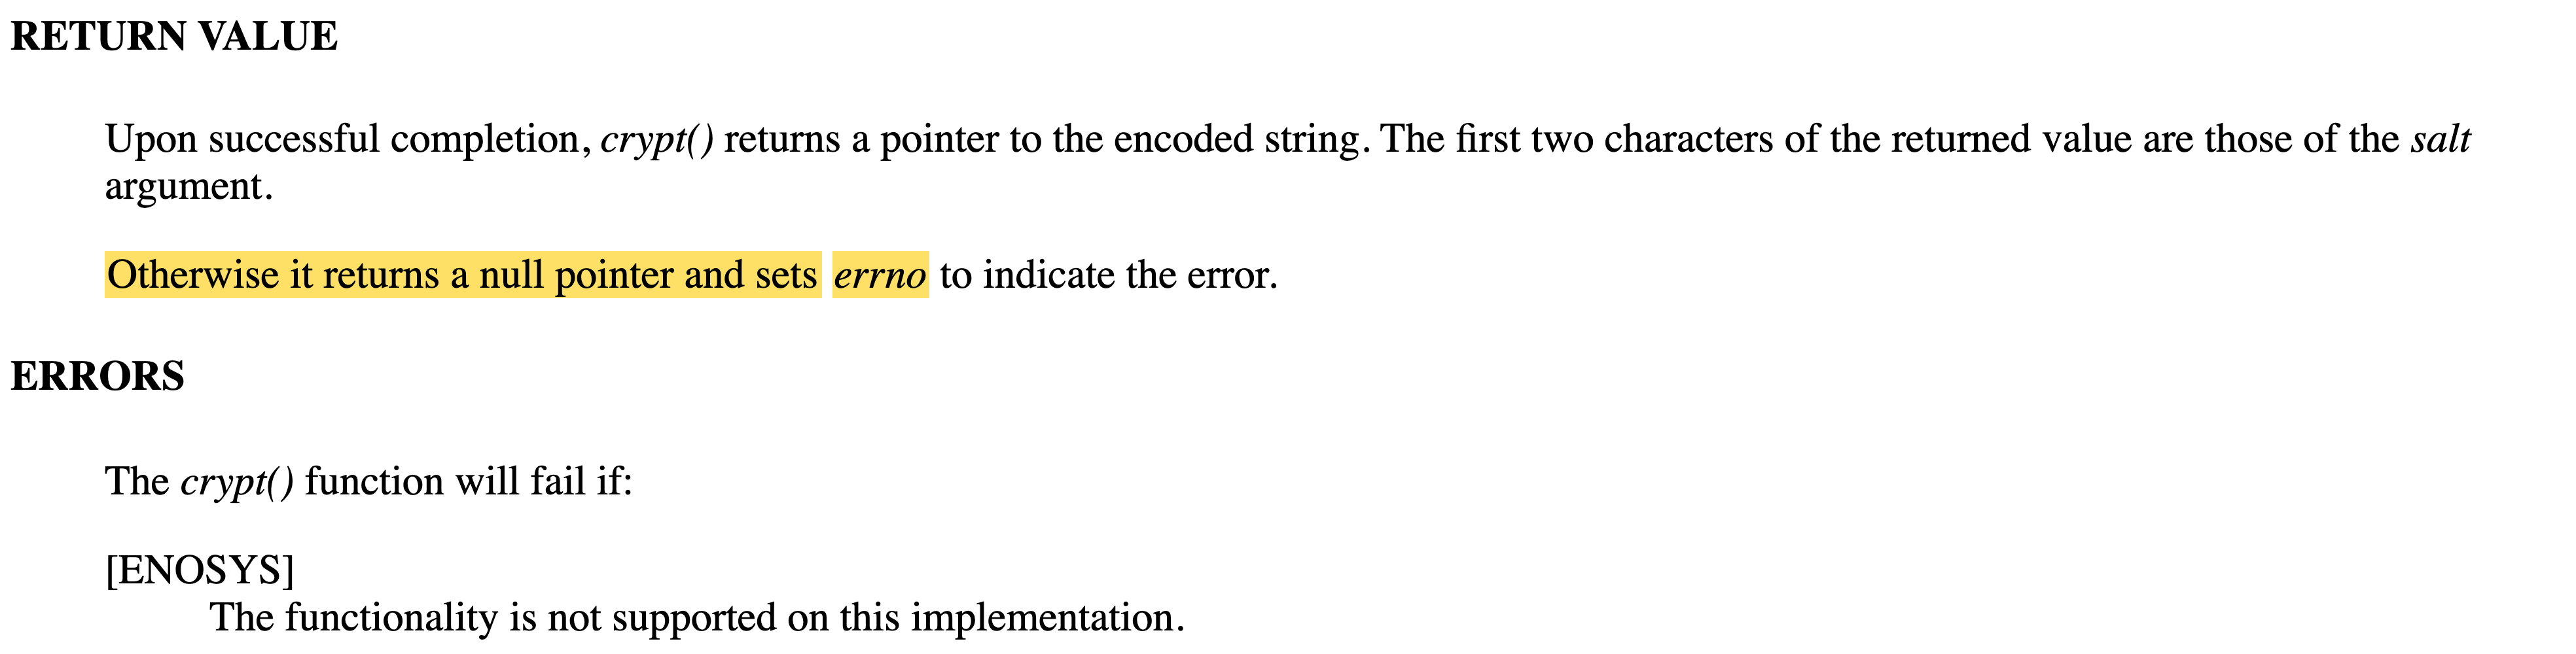
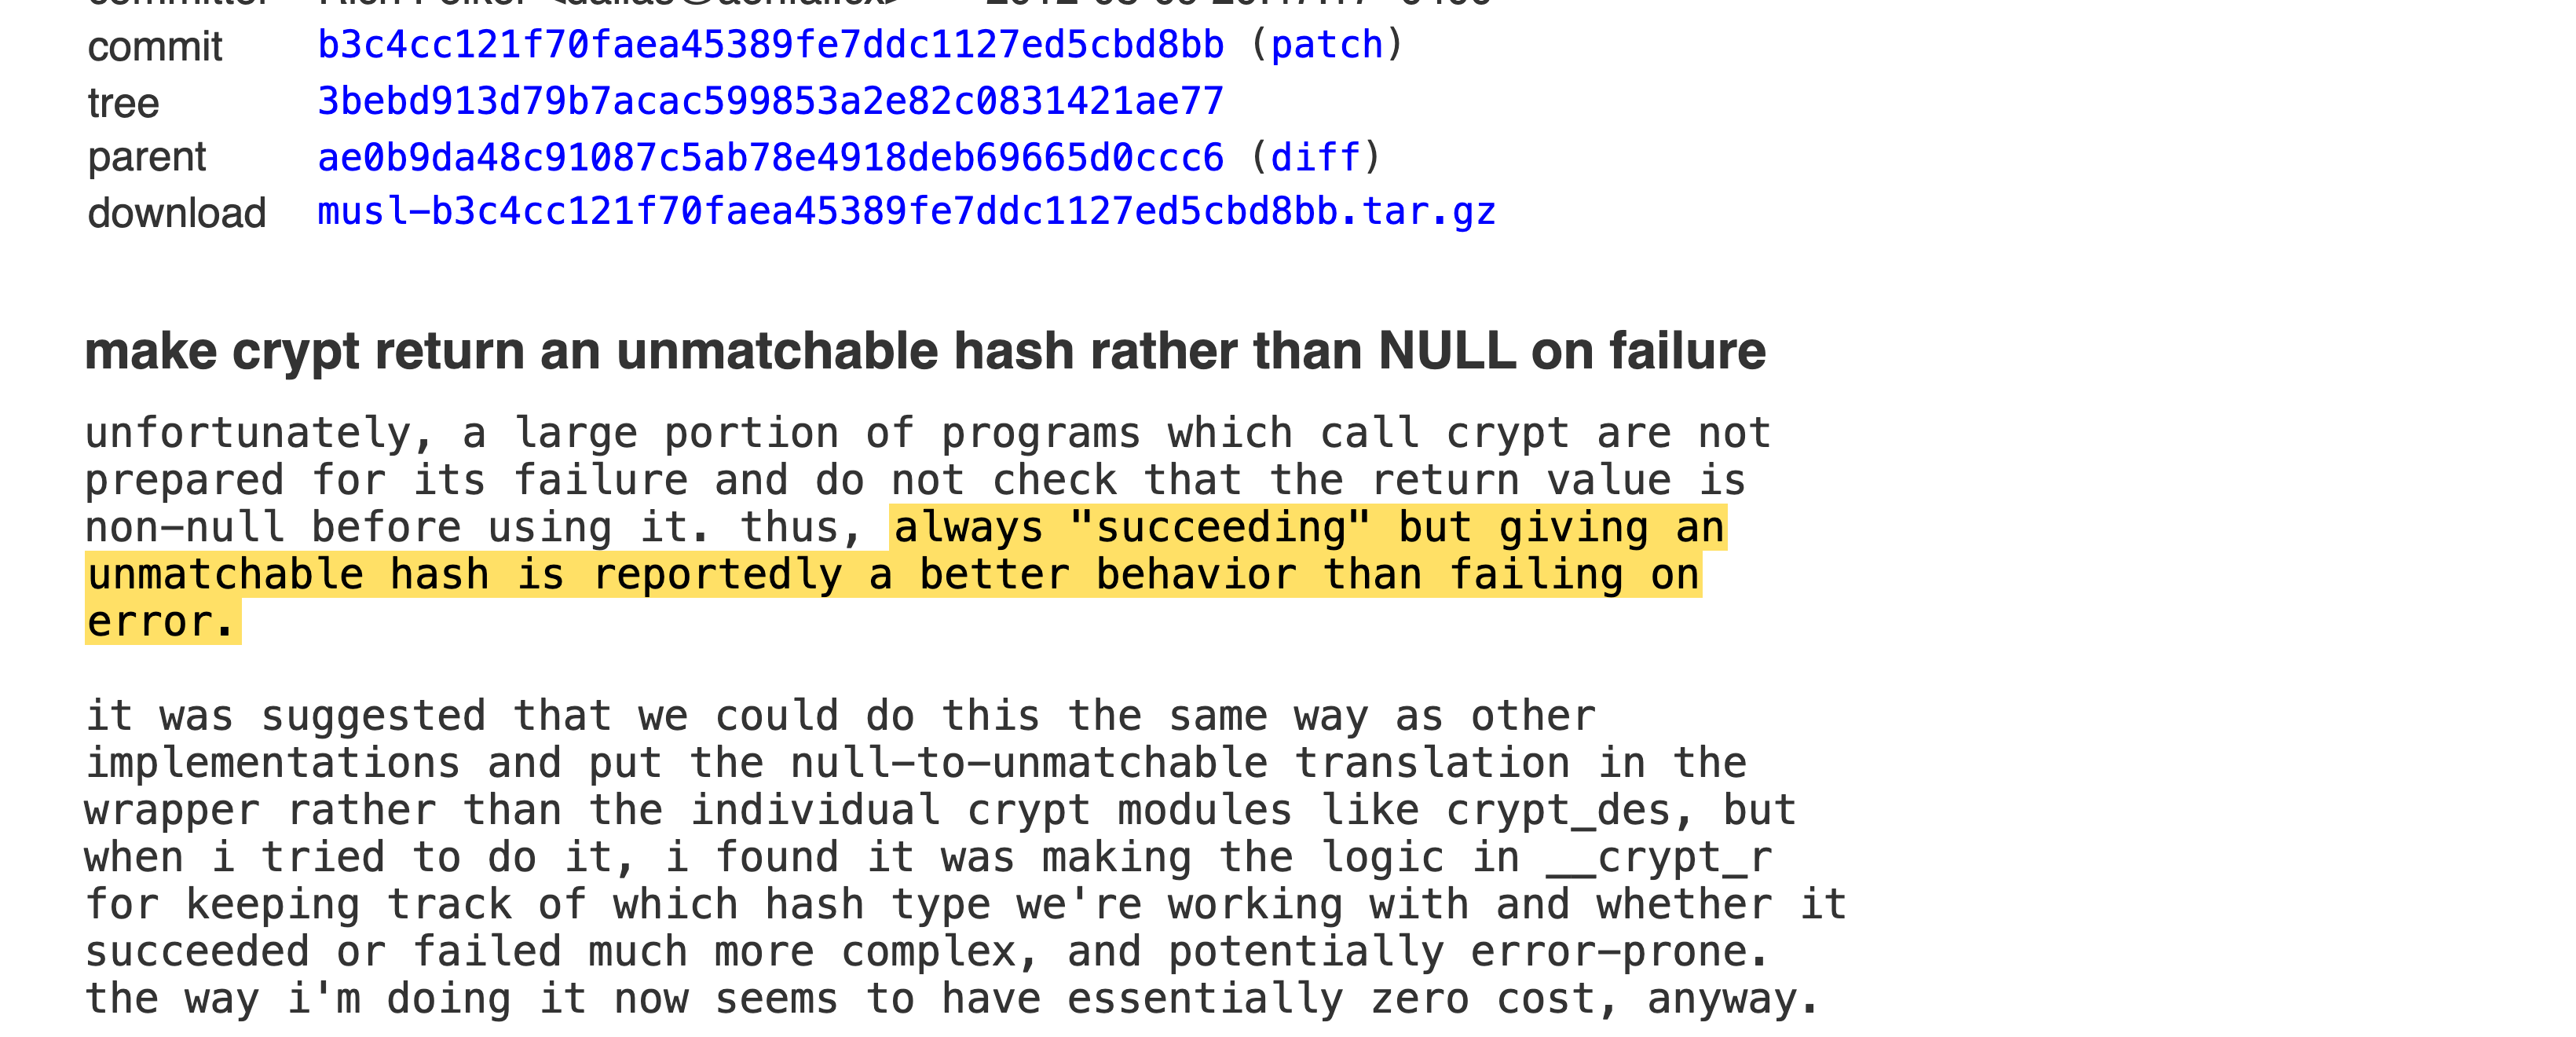
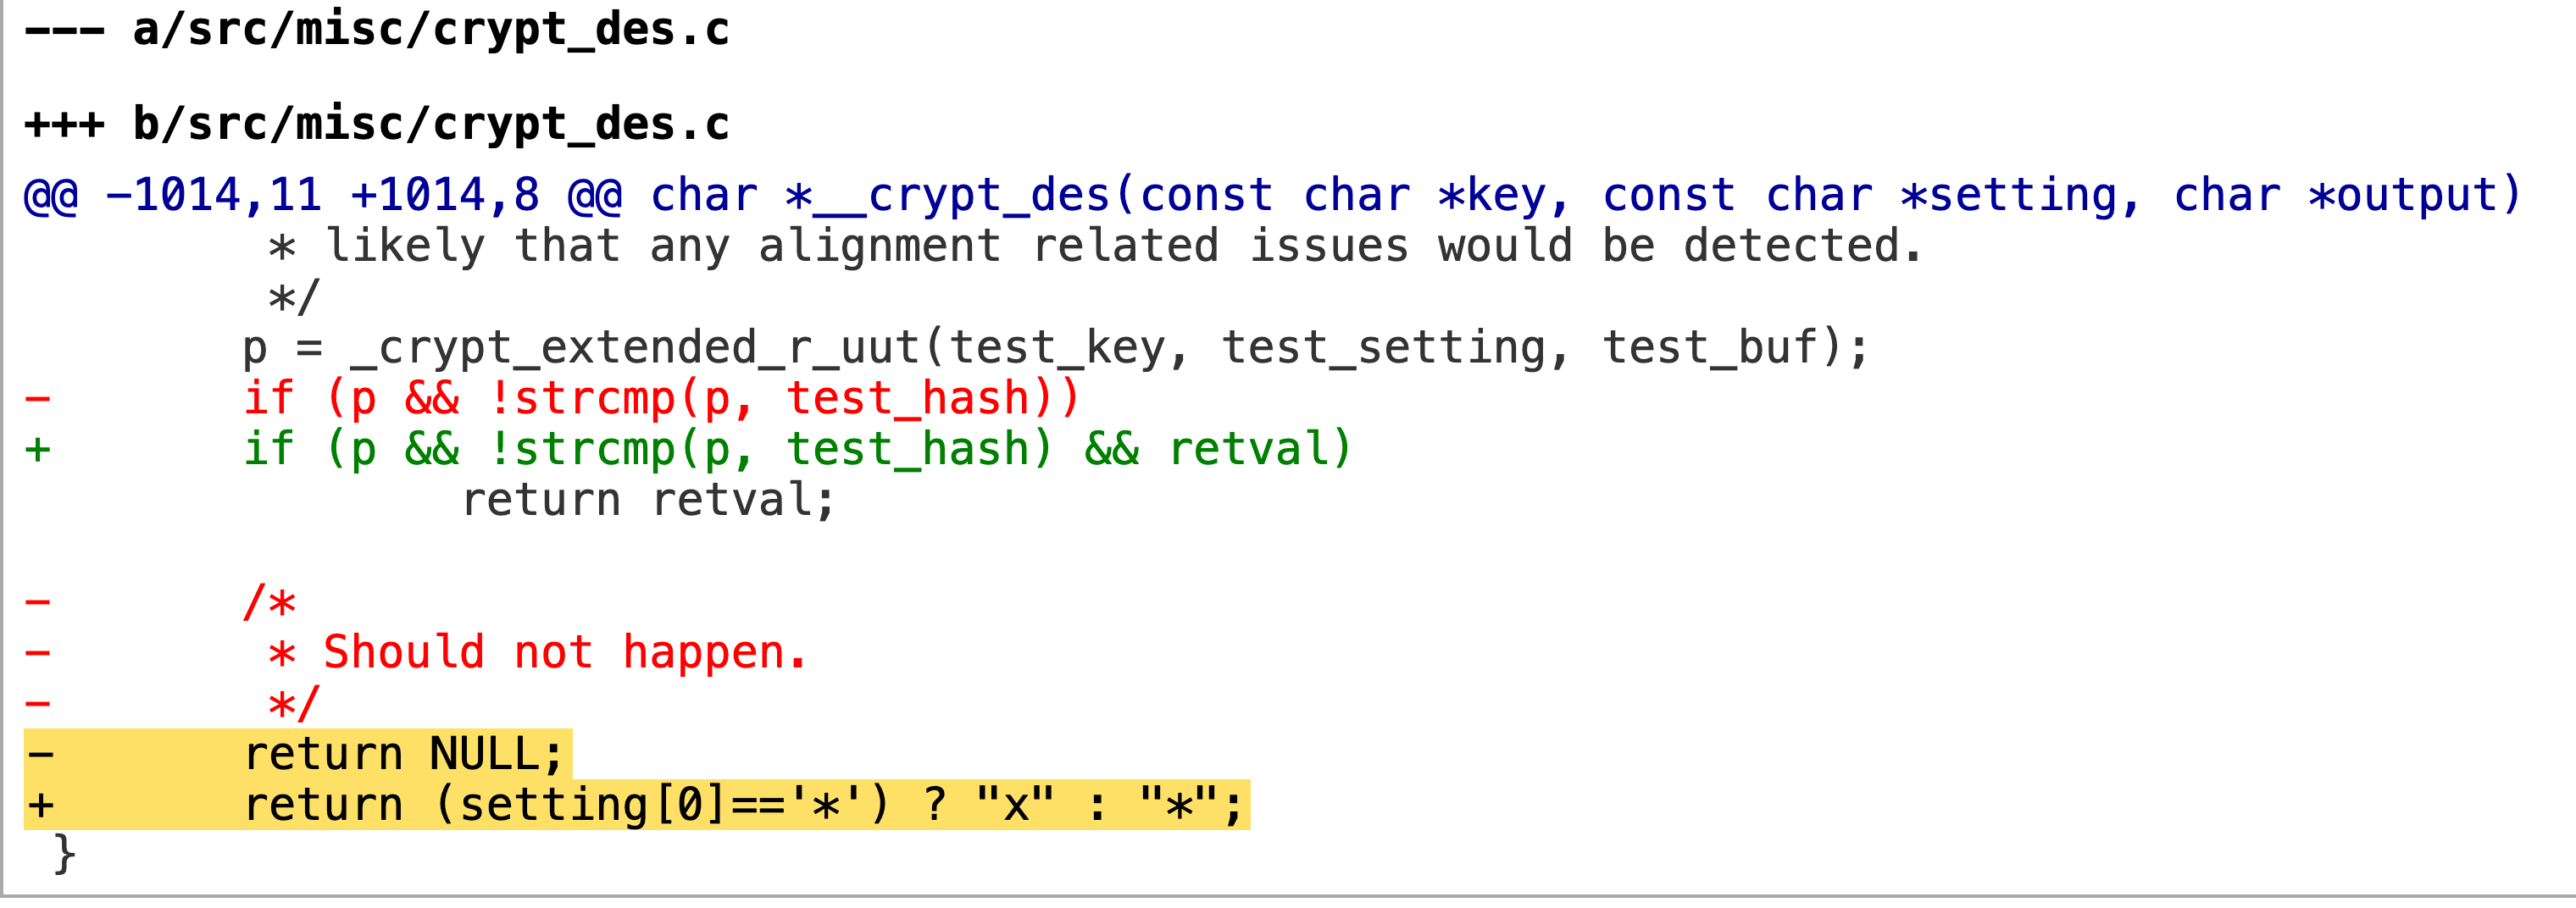
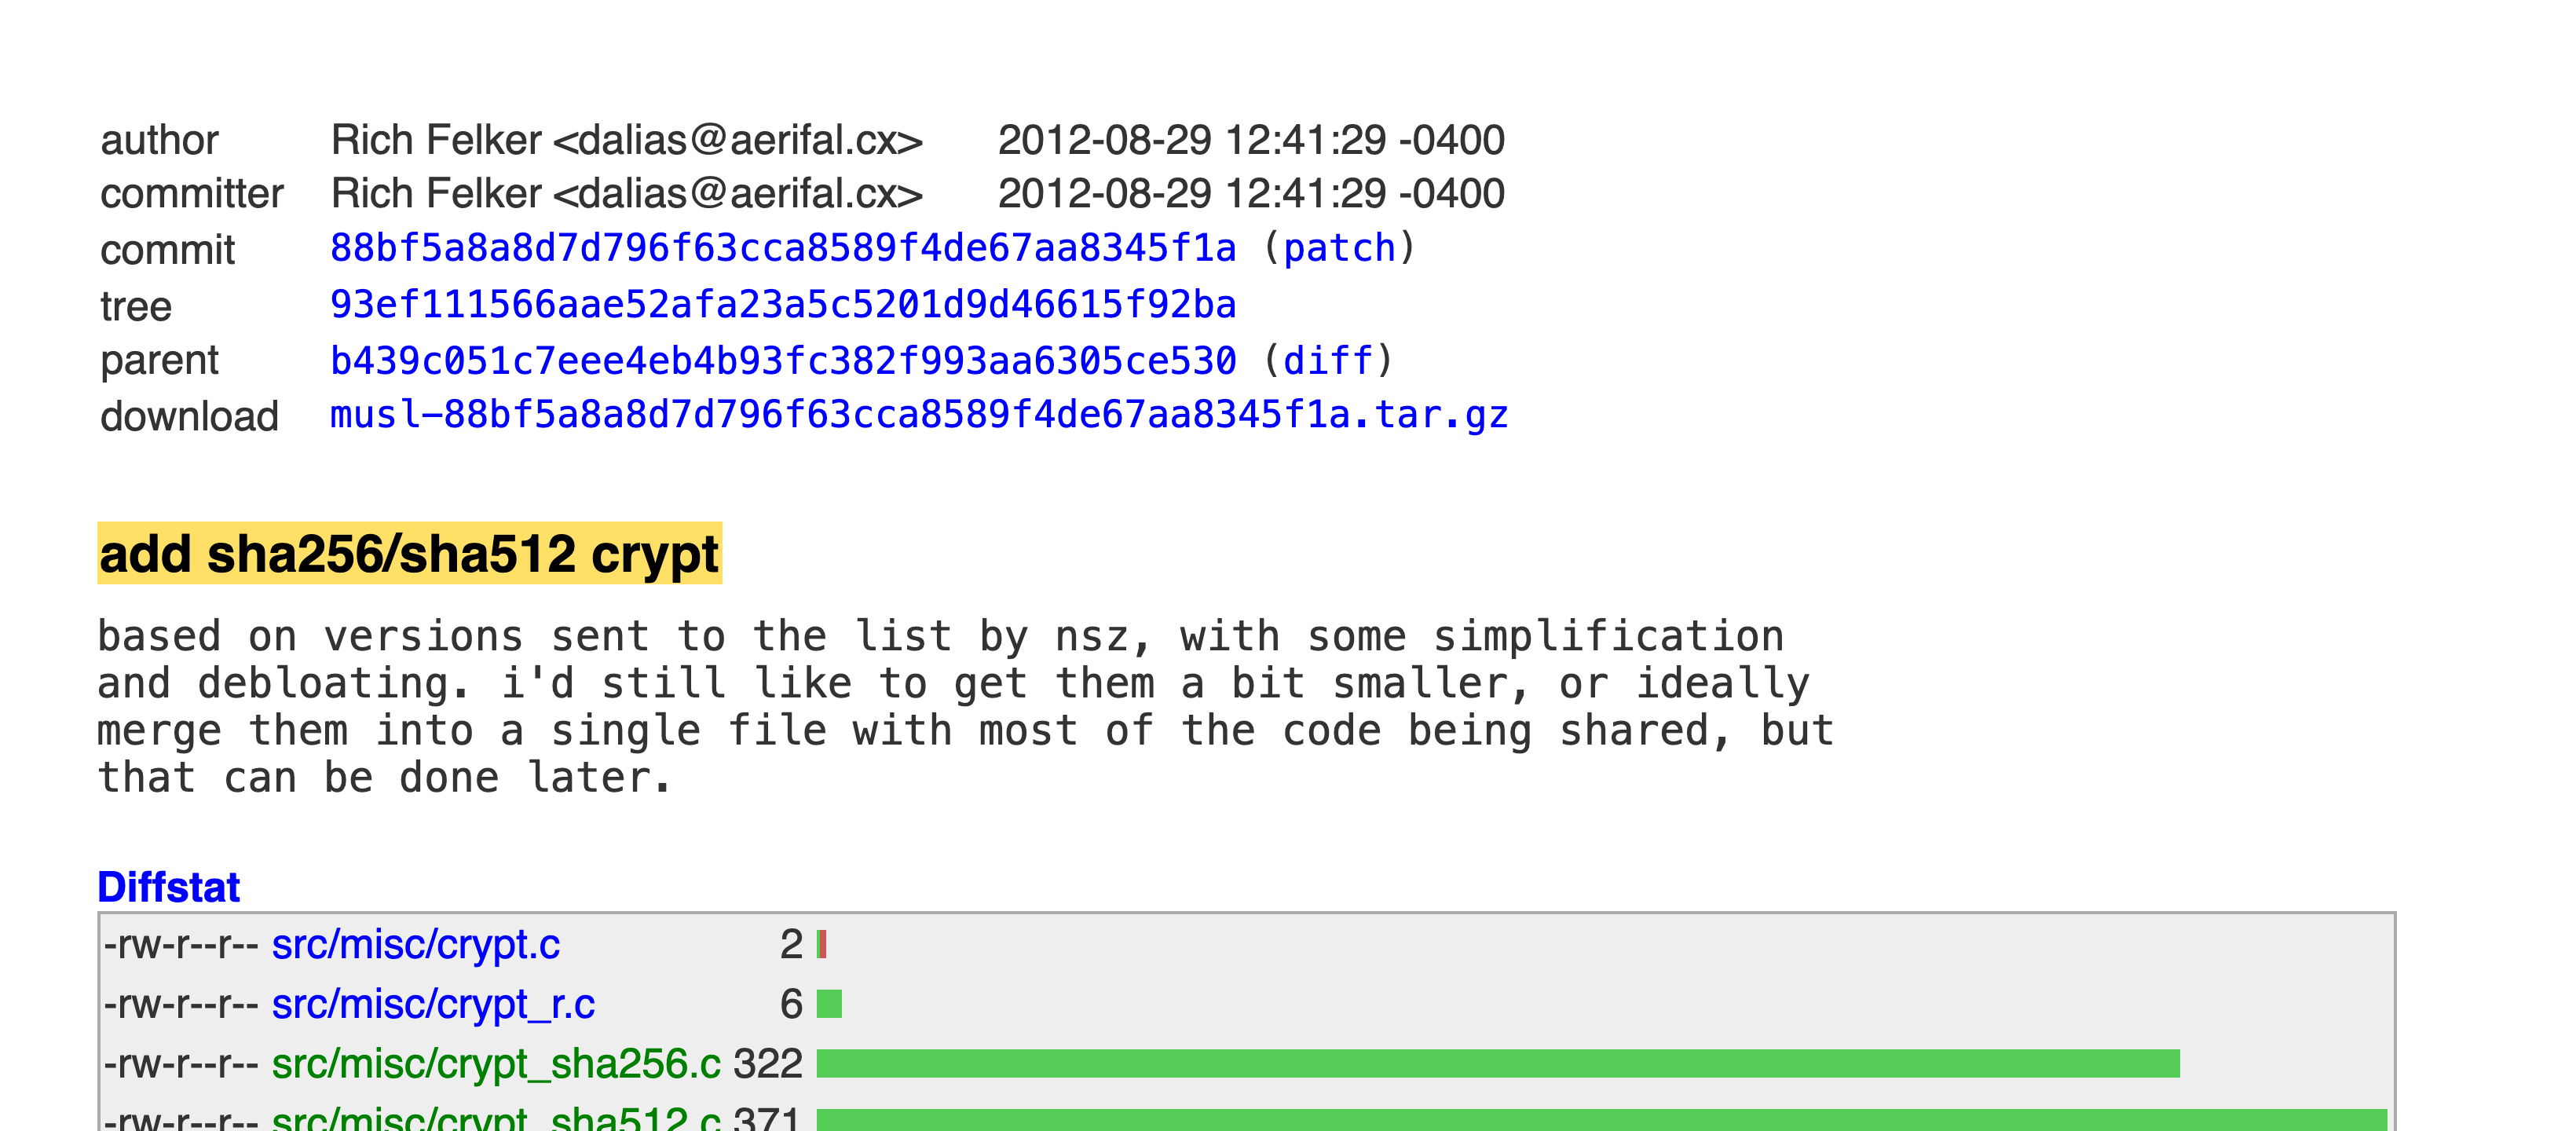
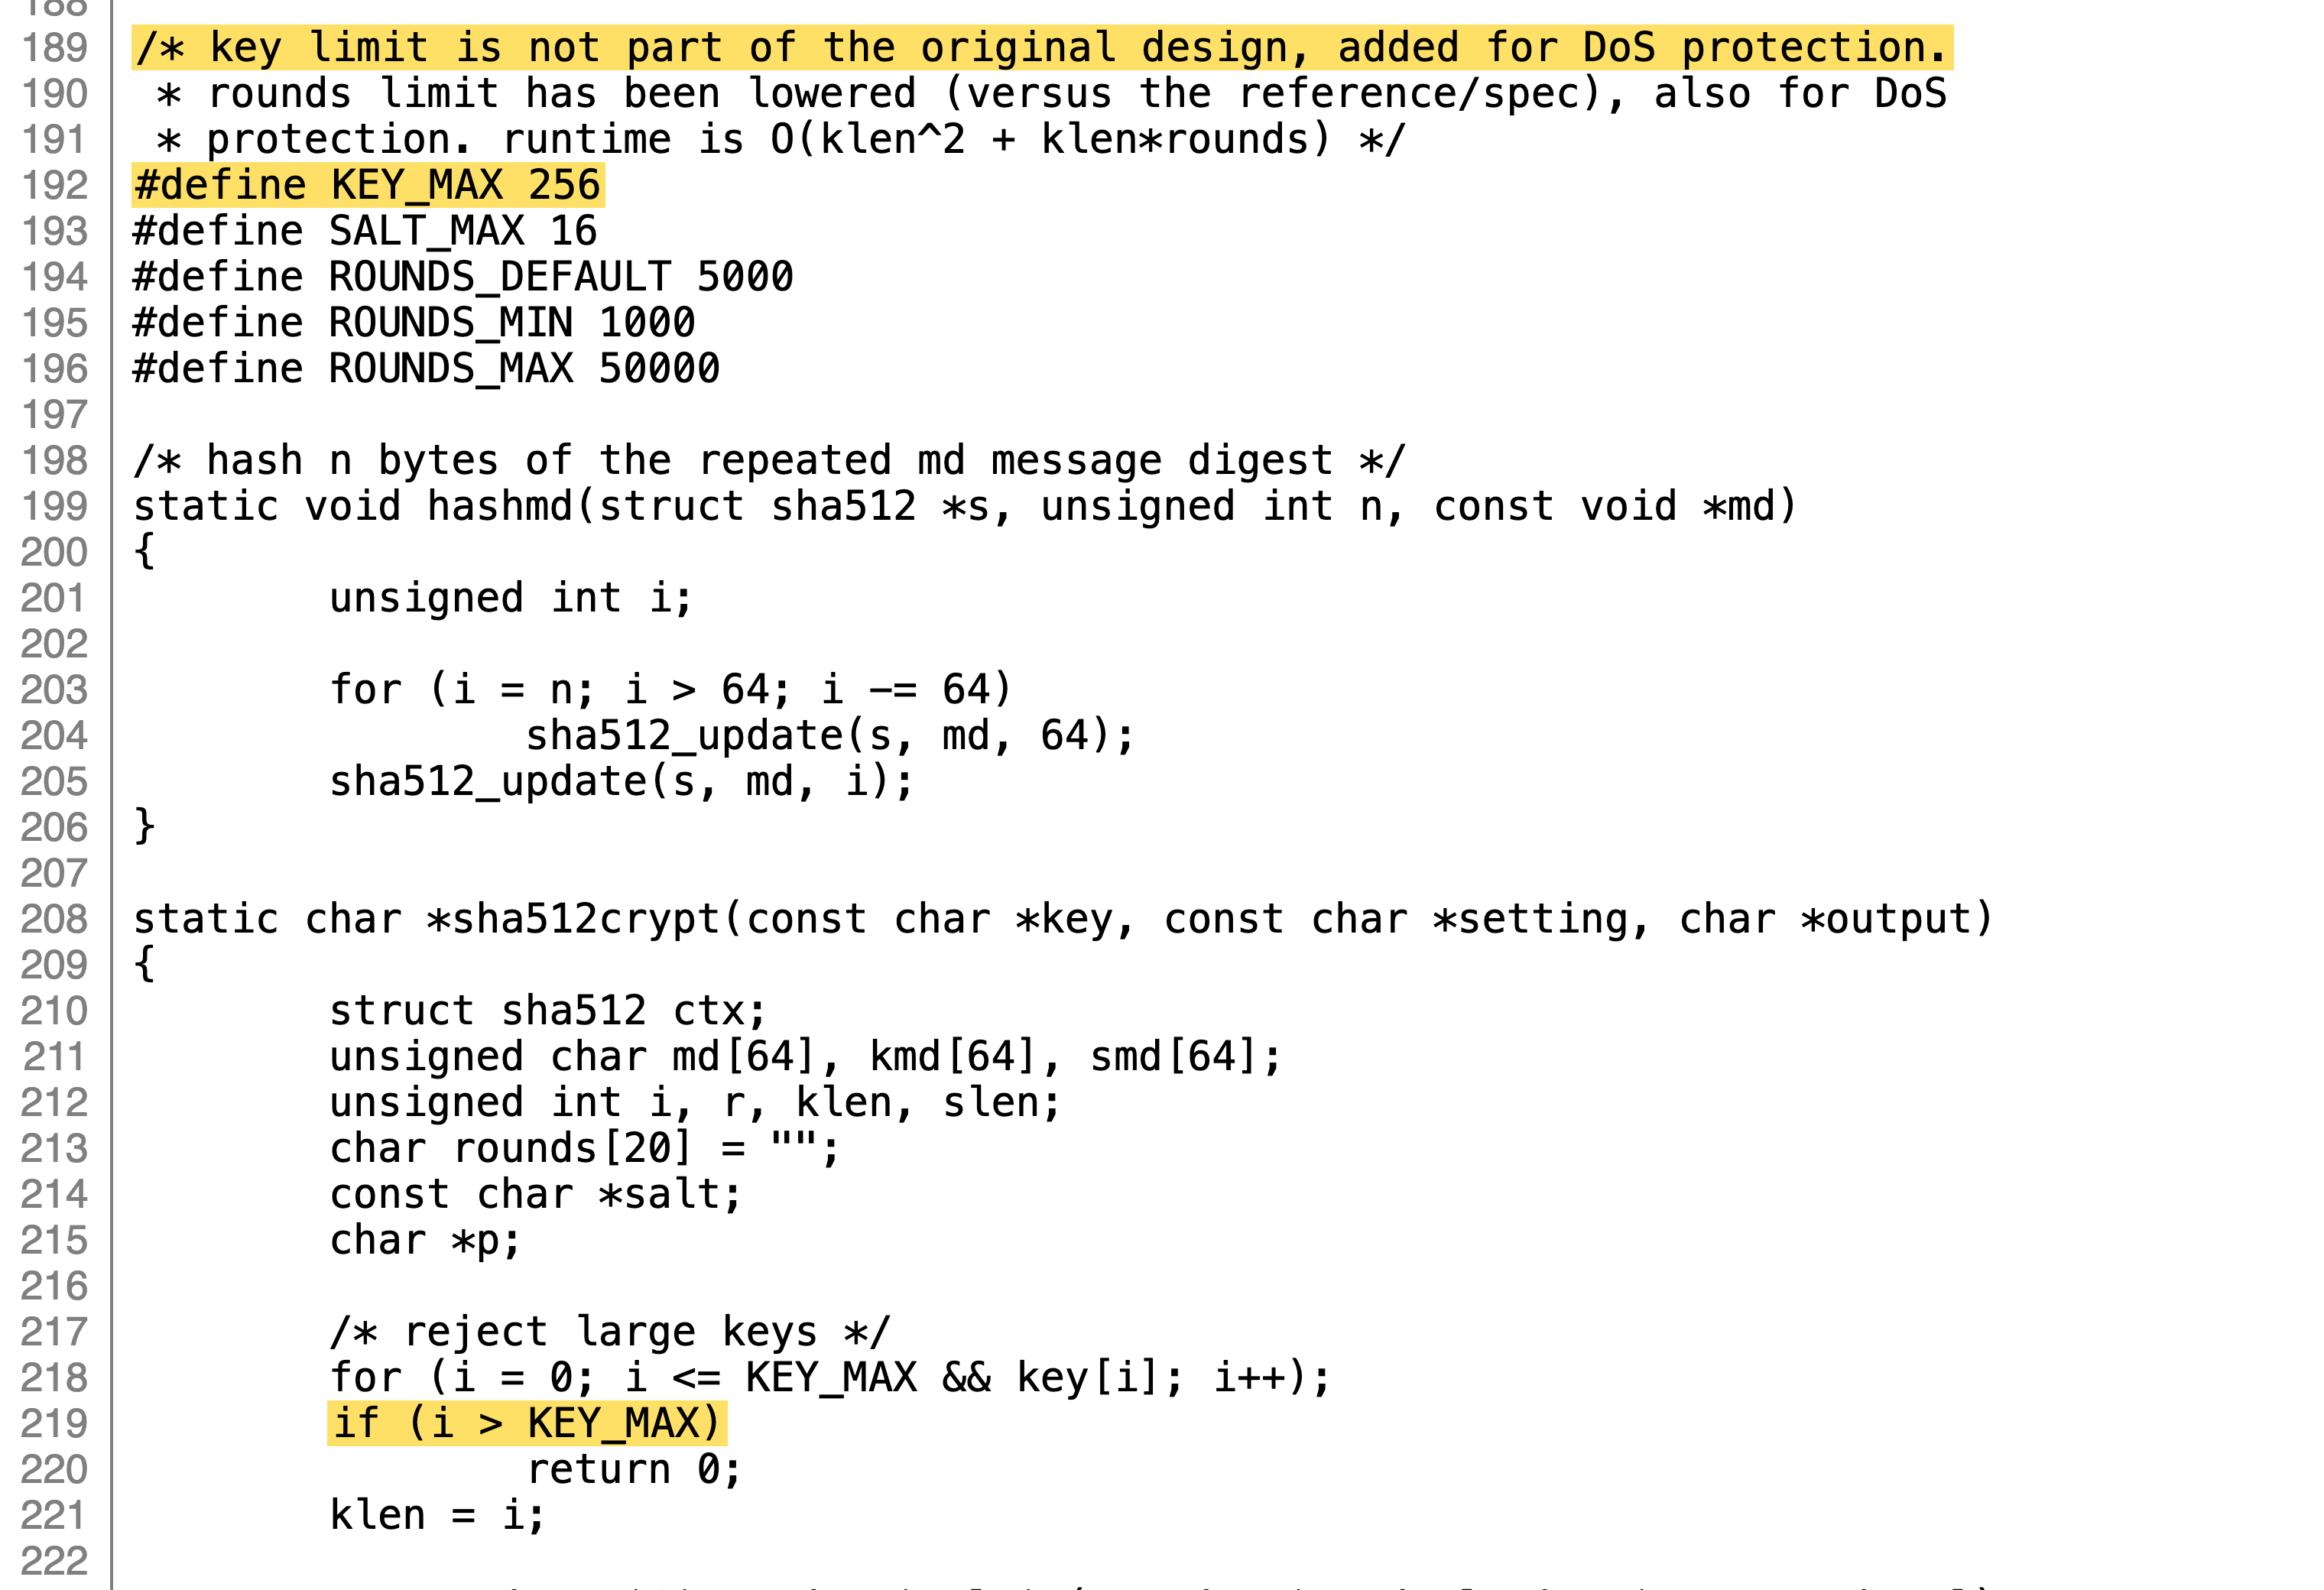
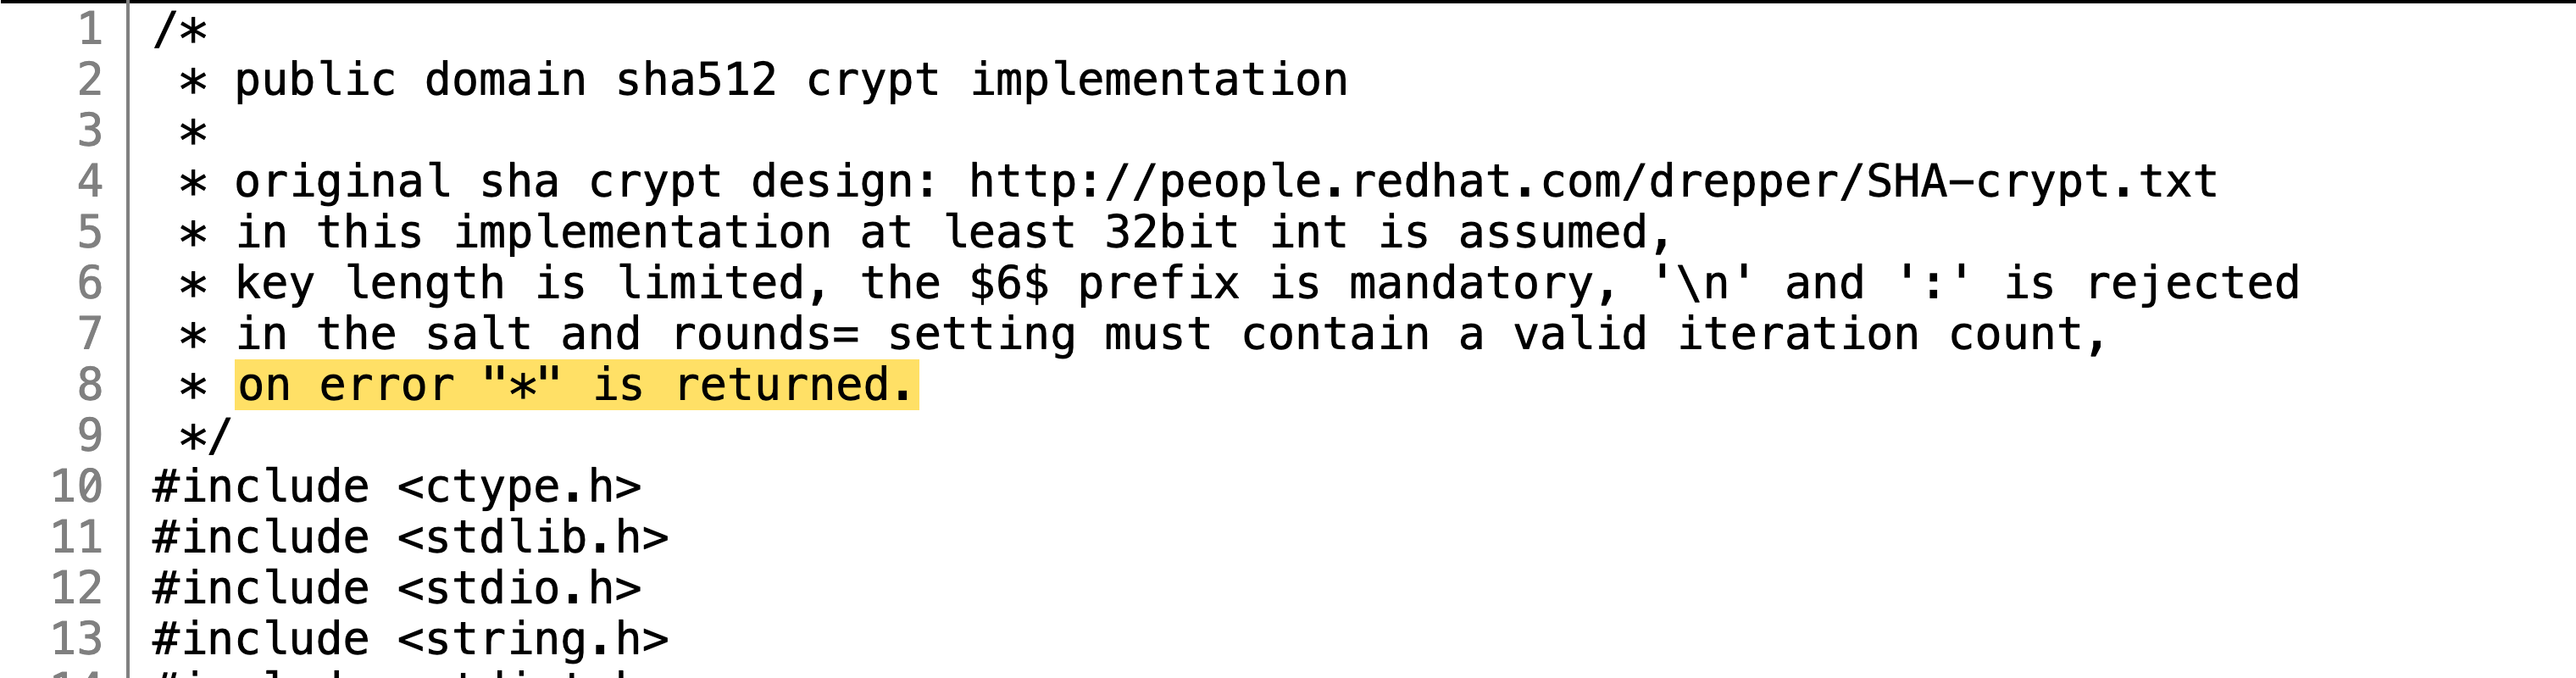
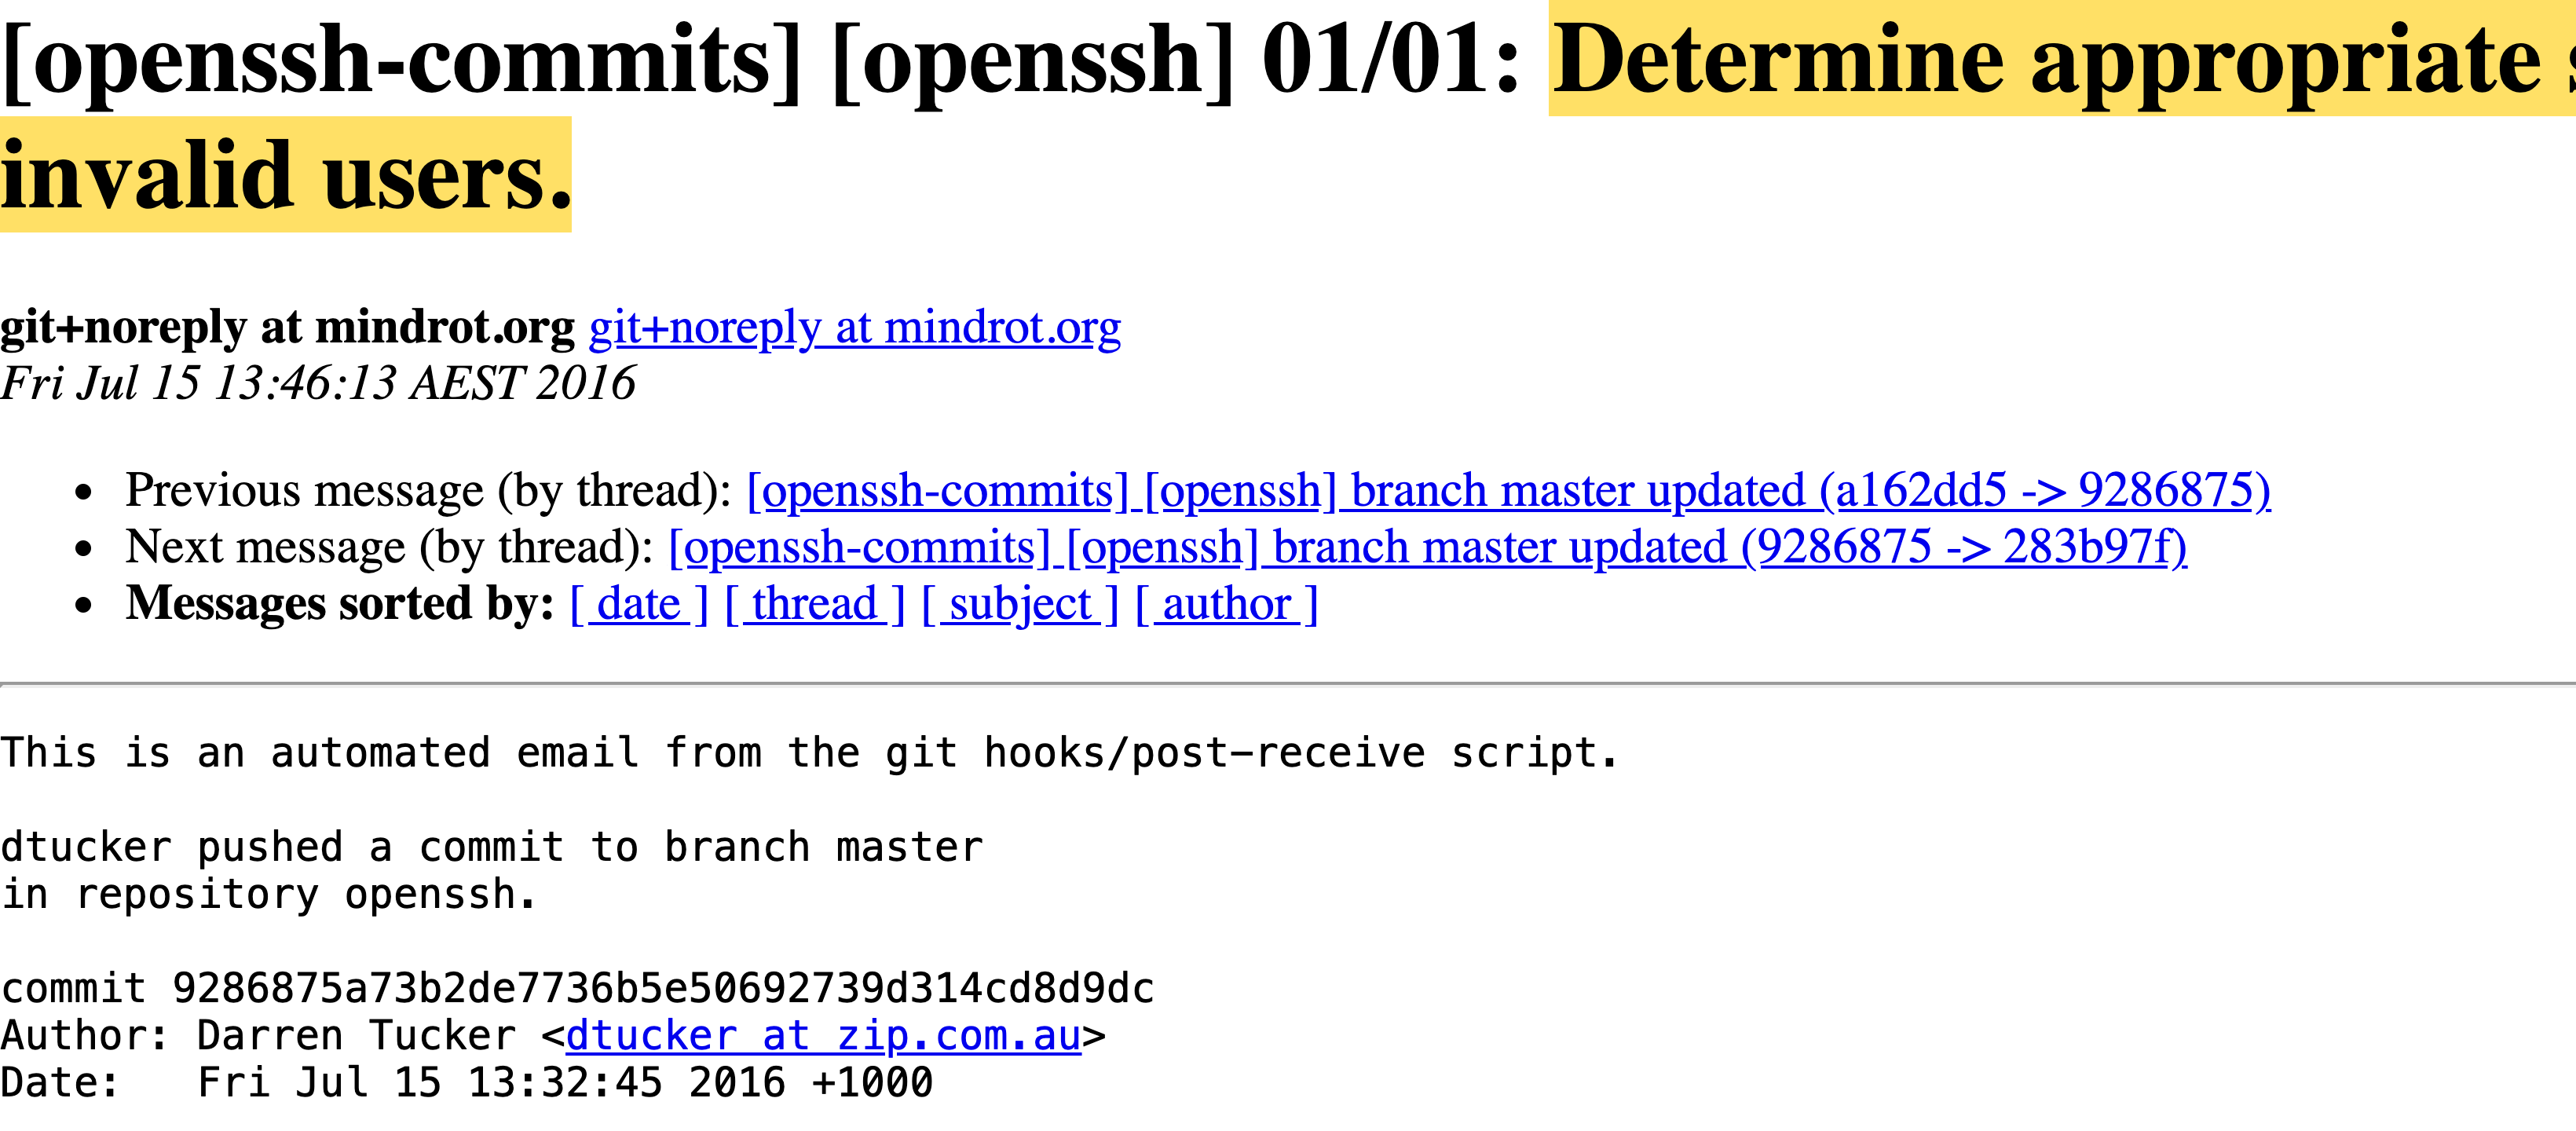
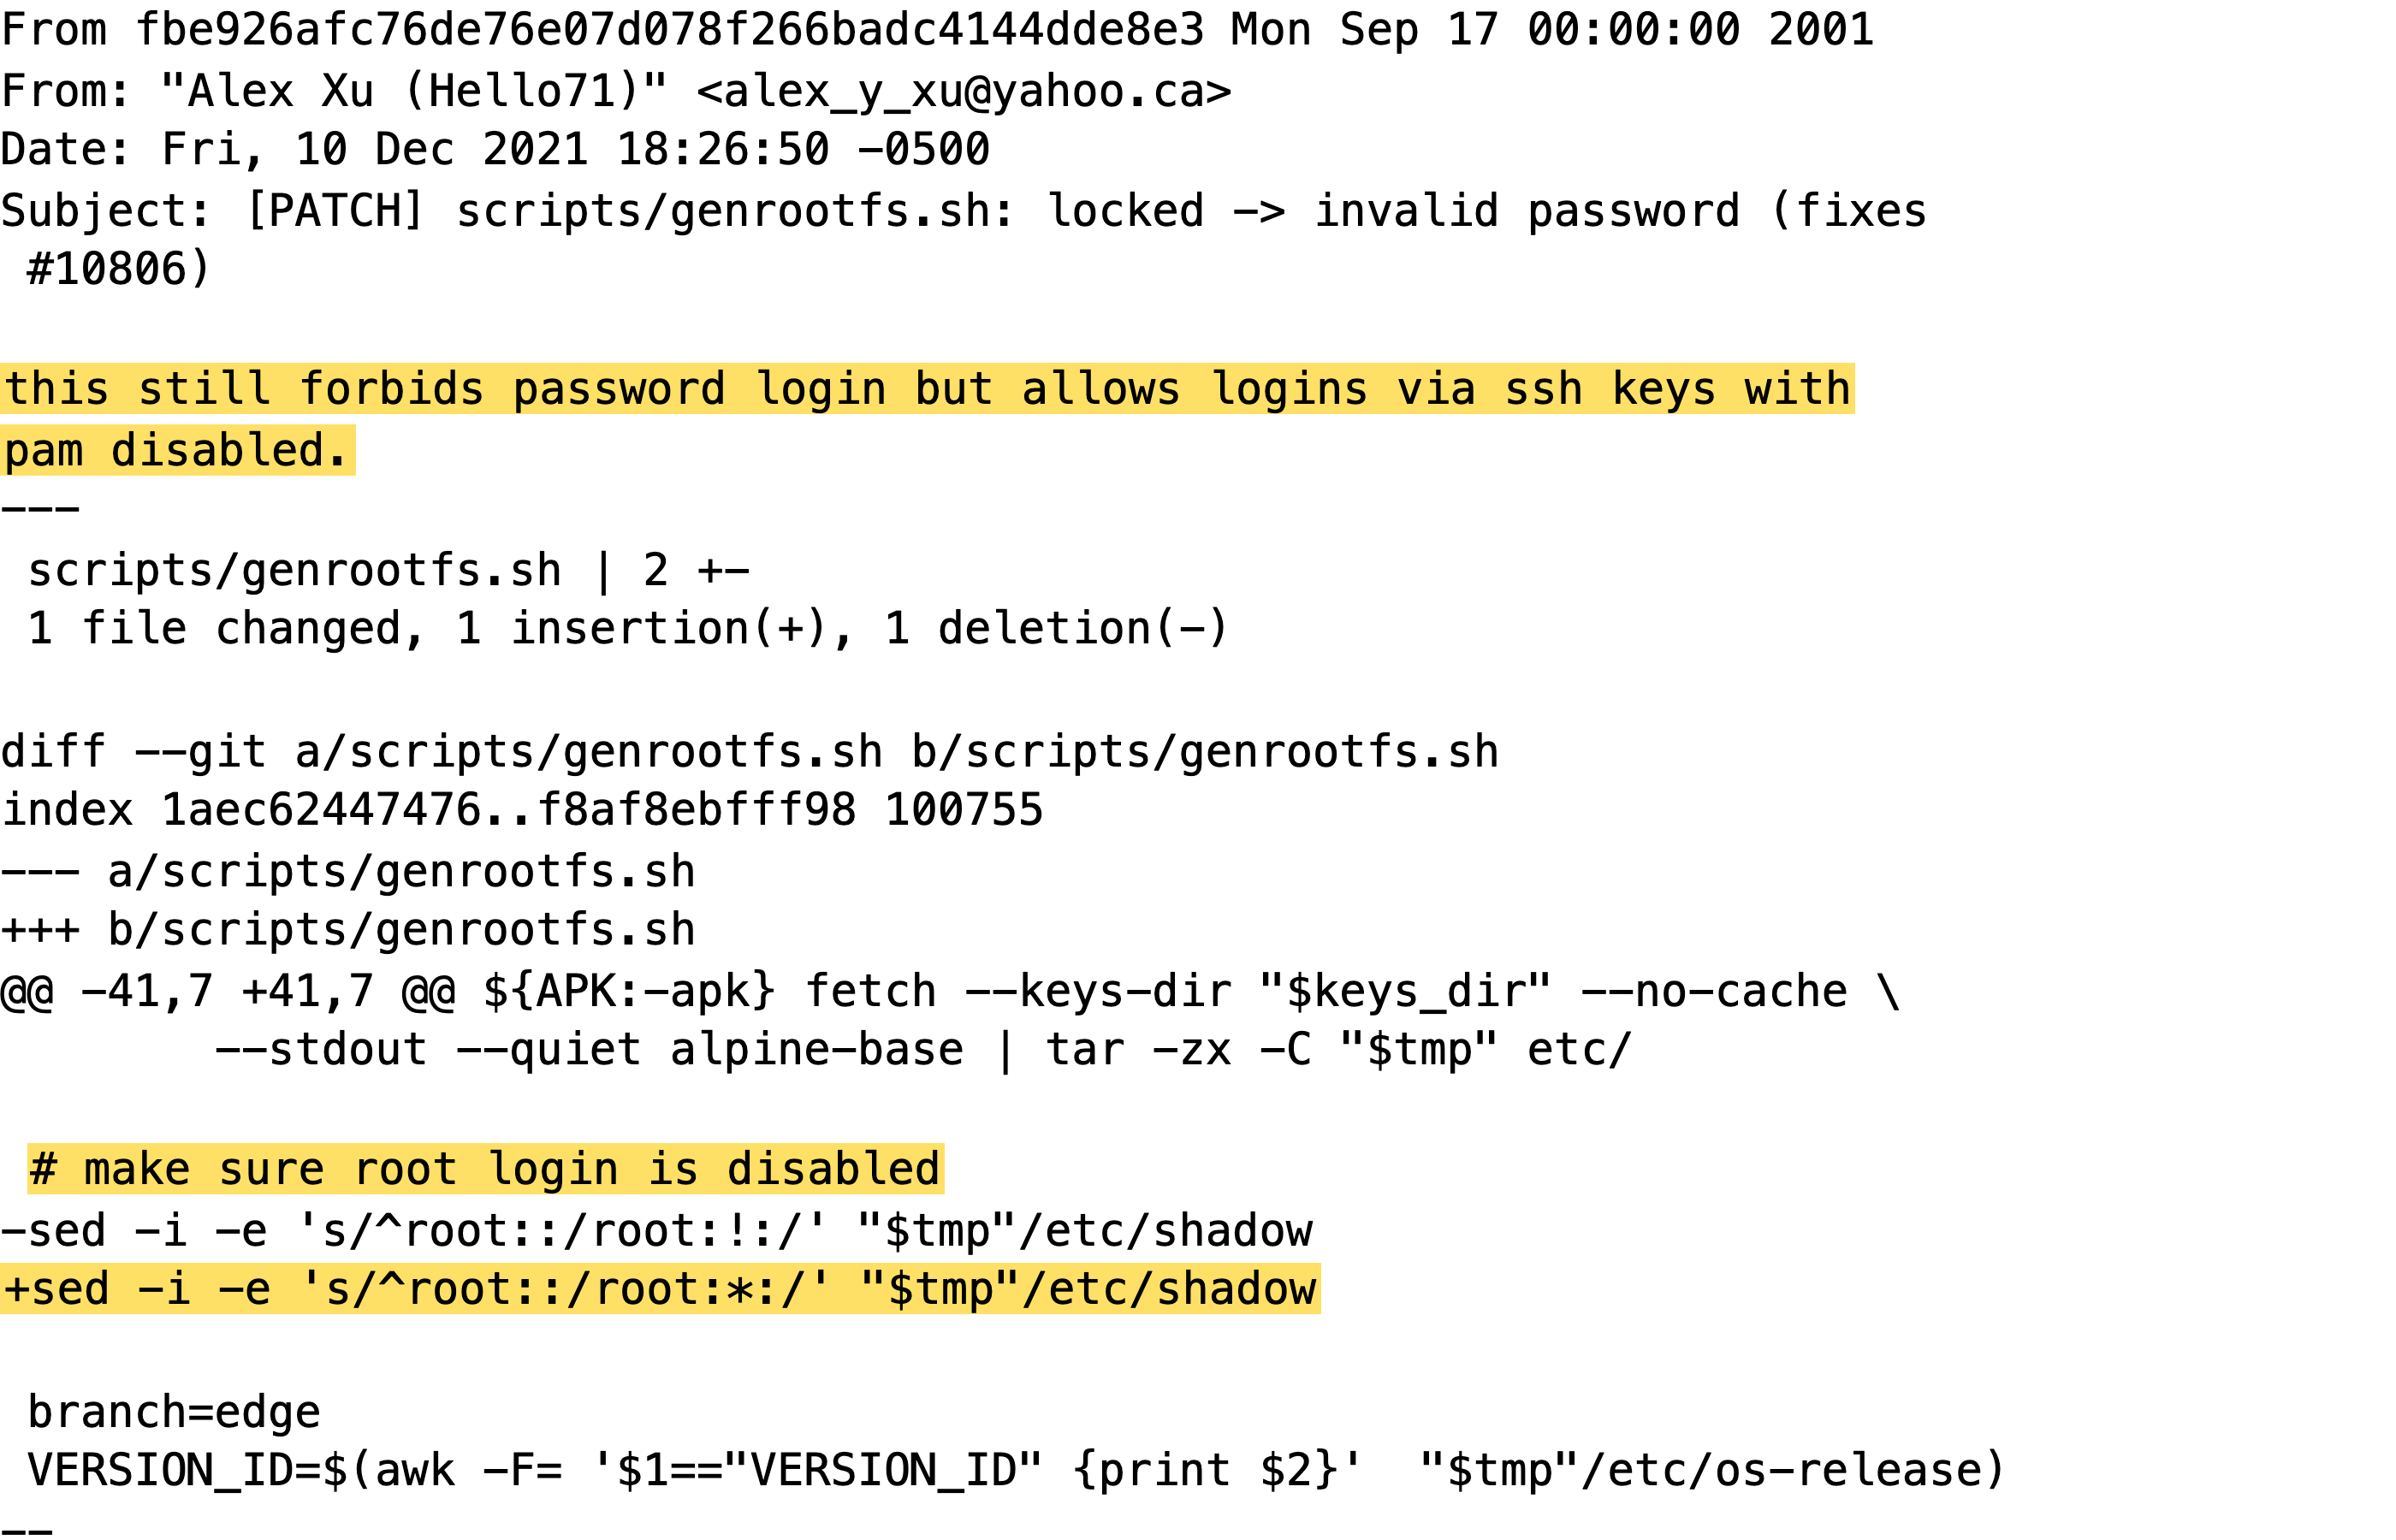
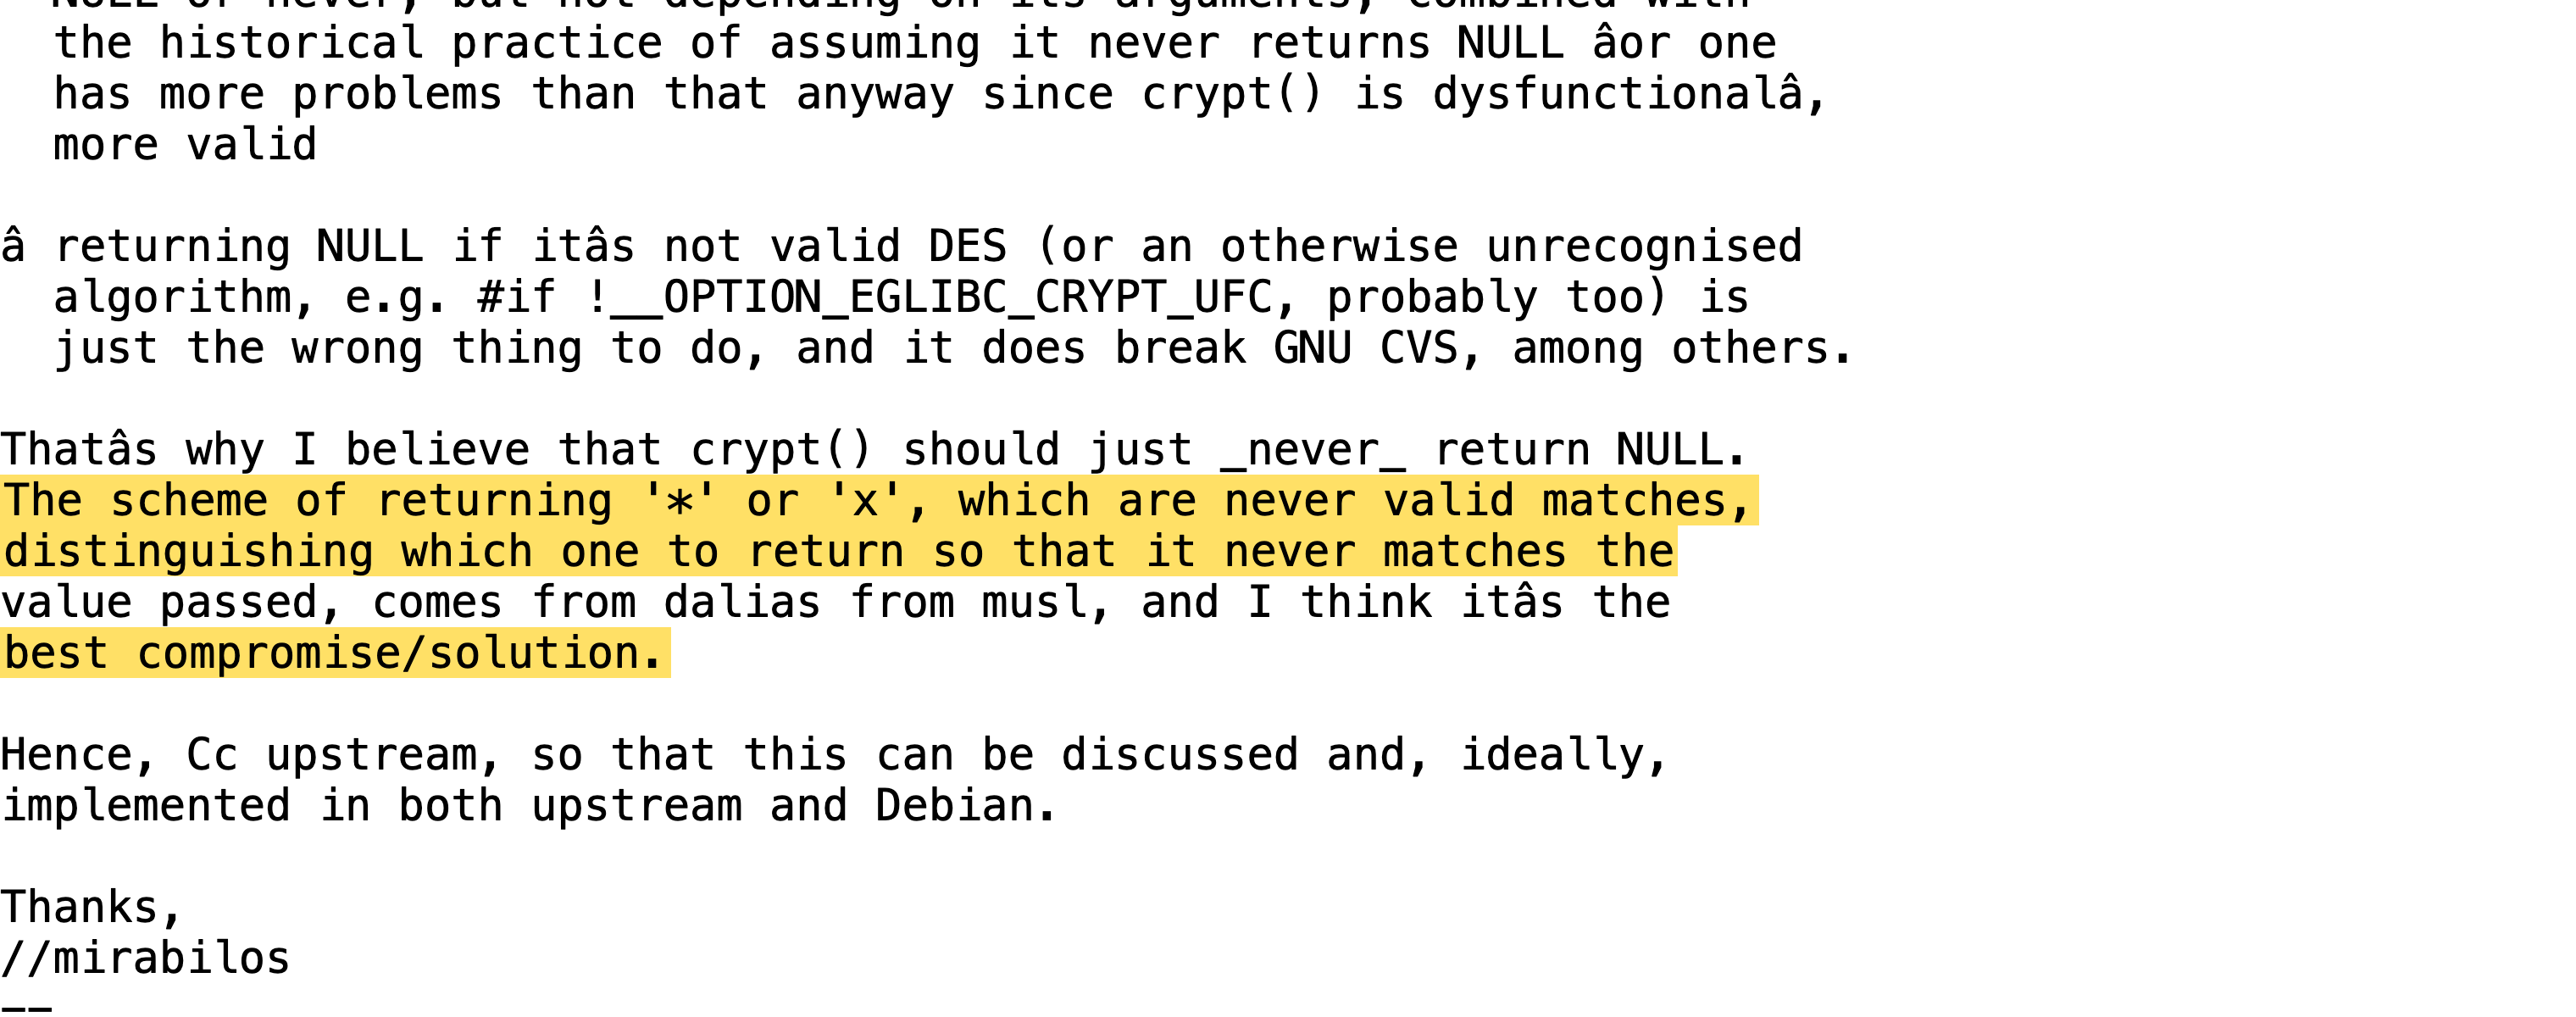
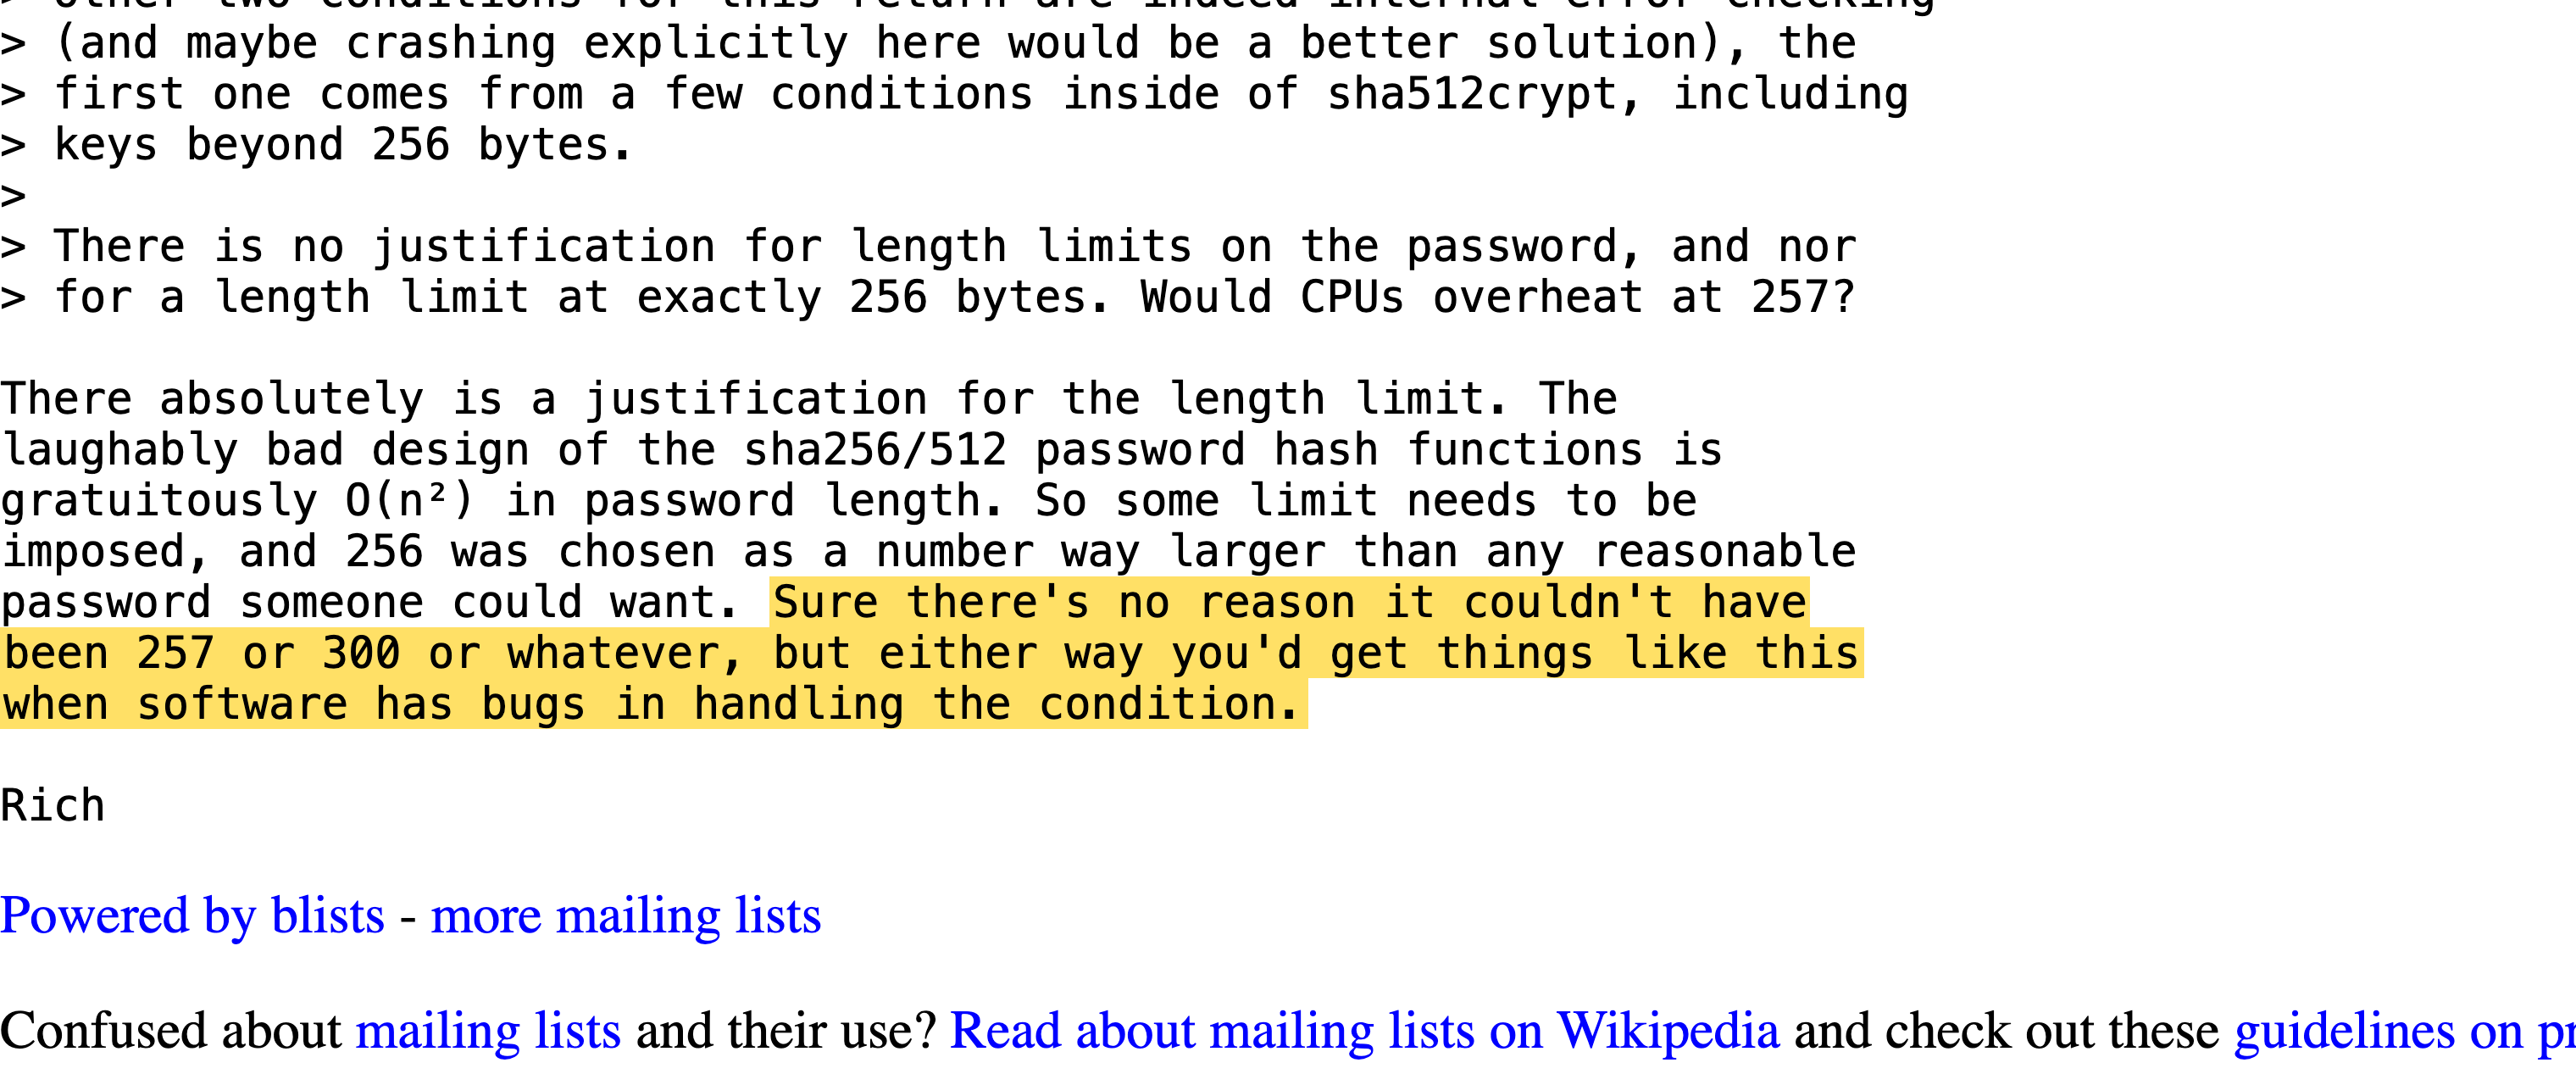
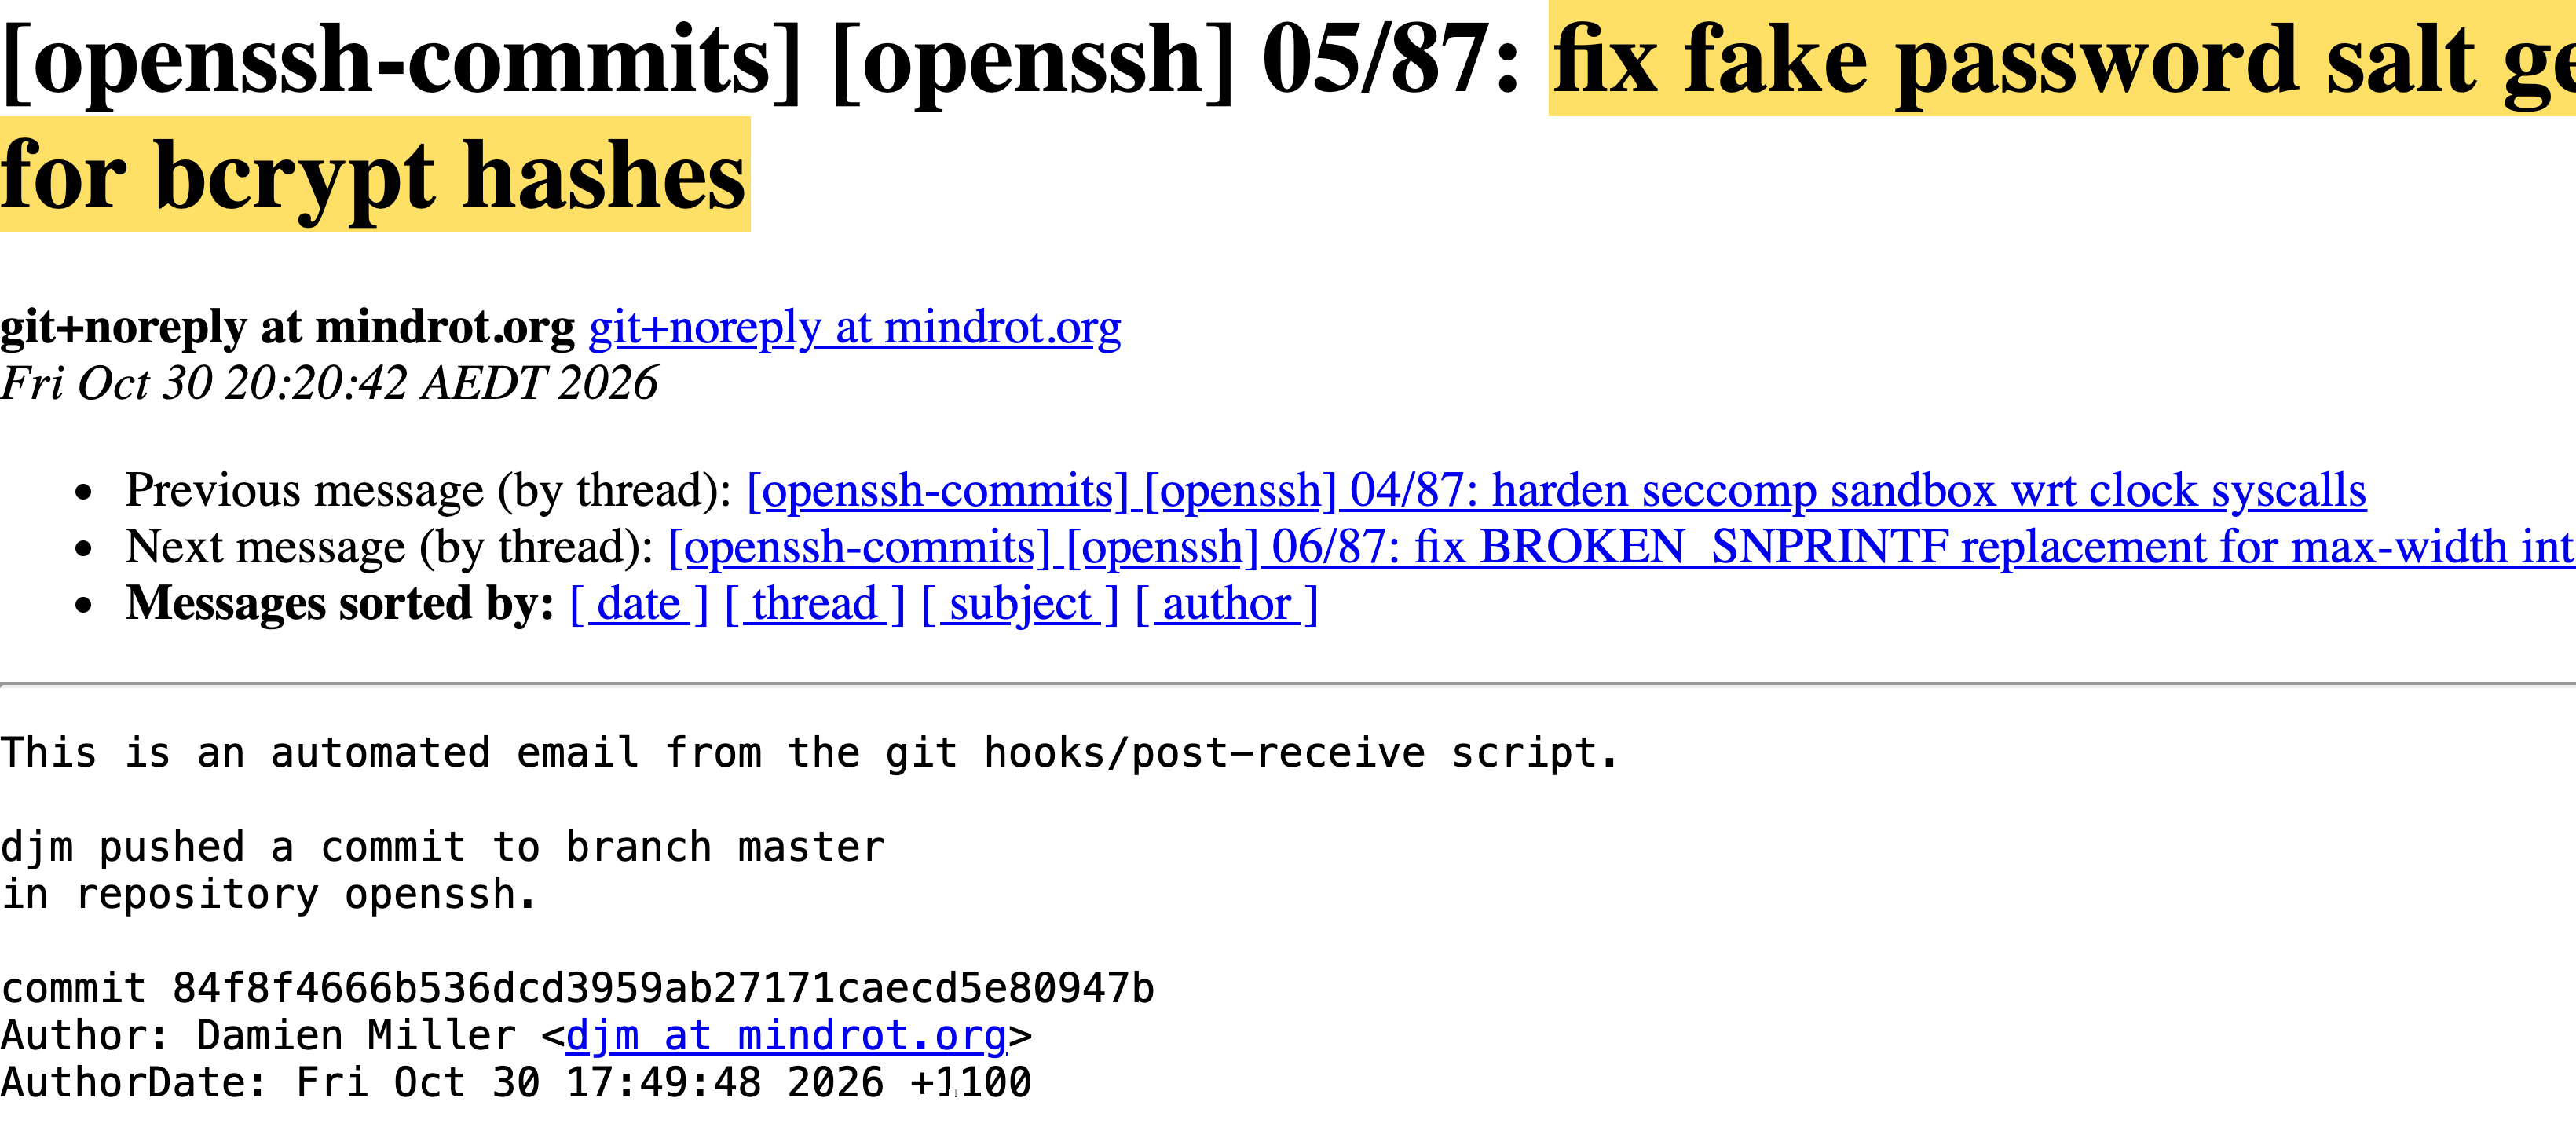
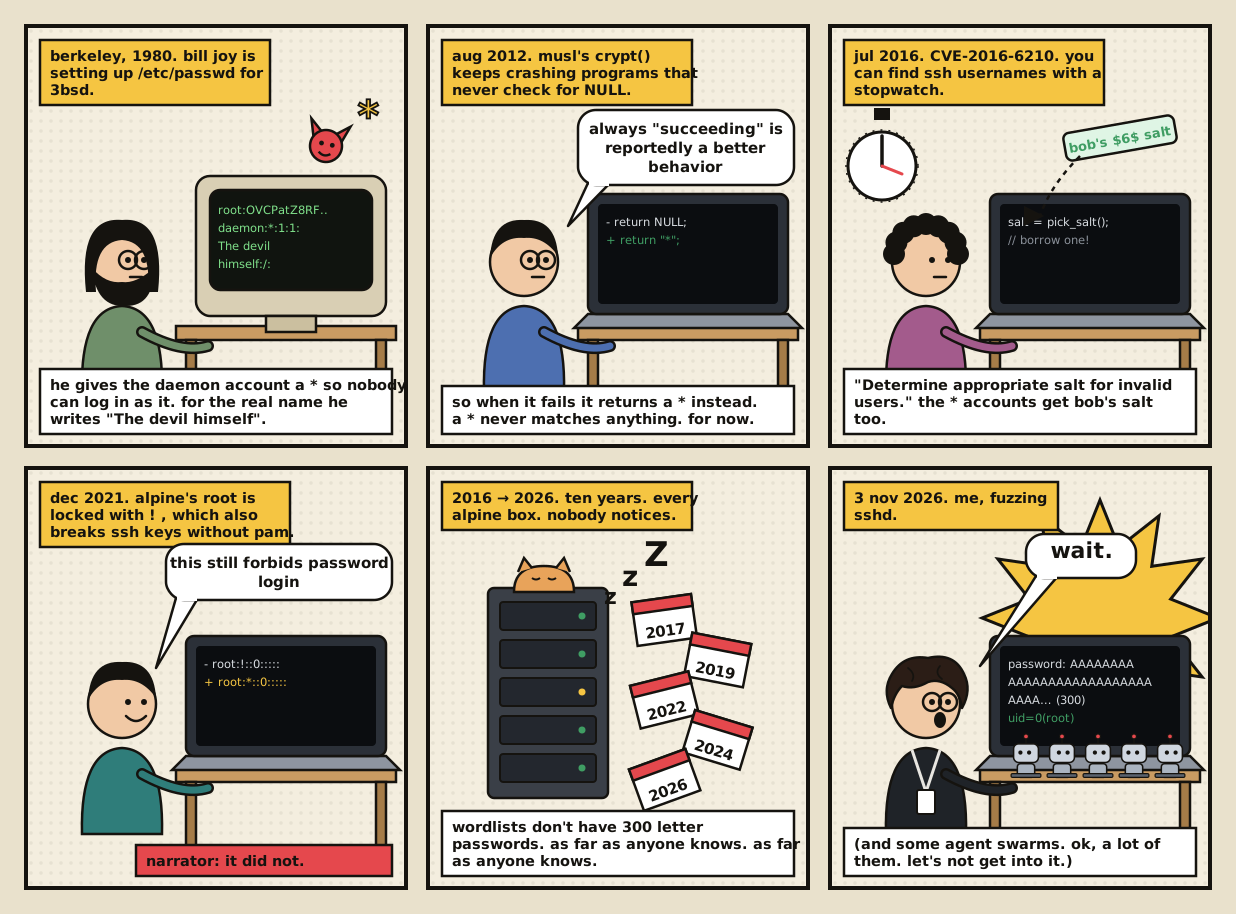
means sha512, `abc` is the salt, the rest is the actual hash\n\nyou type your password, sshd hashes it with that same salt and checks if it comes out identical. same = you're in. that's it\n\nand if the field is just `*`? there's nothing to match. type whatever you want, it's never getting you in\n\n1990s\n\n## the fine print\n\none more rule. if `crypt()` can't do its job, it returns NULL. like if the salt asks for some algorithm the system doesn't have, there's nothing to compute, so you get NULL instead of a hash\n\n[the single unix spec · crypt() · 1997 **Address**pubs.opengroup.org/onlinepubs/7908799/xsh/crypt.html ![Image 2: RETURN VALUE: Upon successful completion, crypt() returns a pointer to the encoded string. Otherwise it returns a null pointer and sets errno to indicate the error.](https://sshhole.com/receipts/posix-crypt.png)](https://pubs.opengroup.org/onlinepubs/7908799/xsh/crypt.html)\npretty clear.\n\nexcept a lot of programs never check for NULL. they just compare whatever `crypt()` gives back with the stored field, hit the NULL, and crash\n\n2012\n\n## crypt stops saying NULL\n\nso musl (the libc under alpine) goes ok fine, `crypt()` just won't return NULL anymore. if it fails, it returns a single character instead. that character can never match a real password, so programs don't crash, they just see a wrong password\n\nnow guess which character they picked for that\n\n\"?\"\n\nyep. the star. again.\n\n[musl · b3c4cc12 · aug 2012 **Address**git.musl-libc.org/cgit/musl/commit/?id=b3c4cc12 ![Image 3: make crypt return an unmatchable hash rather than NULL on failure. always \"succeeding\" but giving an unmatchable hash is reportedly a better behavior than failing on error.](https://sshhole.com/receipts/musl-b3c4cc12.png)](https://git.musl-libc.org/cgit/musl/commit/?id=b3c4cc121f70faea45389fe7ddc1127ed5cbd8bb)\n\"reportedly.\"\n\n[musl · b3c4cc12 · the diff **Address**git.musl-libc.org/cgit/musl/commit/?id=b3c4cc12 ![Image 4: diff of crypt_des.c: removed the comment 'Should not happen.' and 'return NULL;', added: return (setting[0]=='*') ? \"x\" : \"*\";](https://sshhole.com/receipts/musl-b3c4cc12-diff.png)](https://git.musl-libc.org/cgit/musl/commit/?id=b3c4cc121f70faea45389fe7ddc1127ed5cbd8bb)\n\"should not happen\" gone, NULL gone, `\"*\"` in\n\n2012\n\n## three weeks later\n\nthen musl adds sha512 crypt. the thing is, sha512crypt gets slower the longer the password is, so someone could send one giant password and keep your server busy for a long time. so musl just caps it at 256 bytes and refuses anything longer\n\n[musl · 88bf5a8a · aug 29 2012 **Address**git.musl-libc.org/cgit/musl/commit/?id=88bf5a8a ![Image 5: add sha256/sha512 crypt. Rich Felker, 2012-08-29.](https://sshhole.com/receipts/musl-88bf5a8a.png)](https://git.musl-libc.org/cgit/musl/commit/?id=88bf5a8a8d7d796f63cca8589f4de67aa8345f1a)\ntwenty days after the \"*\" commit btw\n\n[musl · crypt_sha512.c @ 88bf5a8a **Address**git.musl-libc.org/cgit/musl/tree/src/misc/crypt_sha512.c?id=88bf5a8a ![Image 6: key limit is not part of the original design, added for DoS protection. #define KEY_MAX 256. if (i > KEY_MAX) return 0;](https://sshhole.com/receipts/musl-keymax.png)](https://git.musl-libc.org/cgit/musl/tree/src/misc/crypt_sha512.c?id=88bf5a8a8d7d796f63cca8589f4de67aa8345f1a#n189)\nso past 256 bytes crypt fails. and when crypt fails… it says `\"*\"`.\n\n[musl · crypt_sha512.c **Address**git.musl-libc.org/cgit/musl/tree/src/crypt/crypt_sha512.c ![Image 7: on error \"*\" is returned.](https://sshhole.com/receipts/musl-sha512-header.png)](https://git.musl-libc.org/cgit/musl/tree/src/crypt/crypt_sha512.c#n8)\nliterally in the comment the whole time\n\n2016\n\n## sshd borrows bob's salt\n\nCVE-2016-6210. ask sshd about a user that doesn't exist and it says no instantly, cause there's nothing to hash. real users take a few ms longer. so just time it and you know who exists\n\nthe fix is kinda funny. no real hash to check? sshd grabs some other account's salt and hashes your password anyway, just to waste the same amount of time. still a no, just a slower no\n\n[openssh-commits · jul 2016 **Address**lists.mindrot.org/pipermail/openssh-commits/2016-July/005428.html ![Image 8: Determine appropriate salt for invalid users.](https://sshhole.com/receipts/openssh-9286875a7.png)](http://lists.mindrot.org/pipermail/openssh-commits/2016-July/005428.html)\n\"for invalid users.\" and also, it turns out, real users with a `*`.\n\n2019 → 2022\n\n## the fix for the fix\n\n**2019.** turns out alpine's docker images had no root password. at all. CVE-2019-5021. alpine fixes it by locking root with `!`\n\nbut without pam, `!` also kills ssh keys. and cloud images log in with keys.\n\n**2022.** alpine 3.16 switches root to `*`. still locked, keys work again\n\n[alpine aports · fbe926af · shipped in 3.16, 2022 **Address**gitlab.alpinelinux.org/alpine/aports/-/commit/fbe926af.patch ![Image 9: this still forbids password login but allows logins via ssh keys with pam disabled. # make sure root login is disabled. root:! becomes root:*](https://sshhole.com/receipts/alpine-fbe926af.png)](https://gitlab.alpinelinux.org/alpine/aports/-/commit/fbe926afc76de76e07d078f266badc4144dde8e3)\nnarrator: it did not.\n\n2016 → 2026\n\n## ten quiet years\n\nwhy did nobody notice? well, maybe someone did. maybe someone pasted the wrong thing into a password prompt, half a slack message or a whole ssh key, and it just let them in. you've never pasted the wrong thing into a password prompt?? amazing. a fresh box with no passwords set isn't affected. a `*` in shadow needs a wrong try first. openssh tests on openbsd and glibc, musl doesn't test sshd, and most distros go through pam, which never even calls crypt for a `*`.\n\nso as far as anyone knows, nobody noticed. as far as anyone knows.\n\nsome people got really close though\n\n[libc-alpha · debian #714219 · 2013 **Address**sourceware.org/legacy-ml/libc-alpha/2013-07/msg00046.html ![Image 10: The scheme of returning * or x, which are never valid matches, comes from dalias from musl, and I think it is the best compromise/solution.](https://sshhole.com/receipts/libc-alpha-2013.png)](https://bugs.debian.org/714219)\na debian dev asks glibc to copy musl's `\"*\"`. six years later debian moves to libxcrypt, which says `\"*0\"`, and closes the bug. one character away.\n\n[musl mailing list · dec 2024 **Address**openwall.com/lists/musl/2024/12/31/2 ![Image 11: Sure there's no reason it couldn't have been 257 or 300 or whatever, but either way you'd get things like this when software has bugs in handling the condition.](https://sshhole.com/receipts/musl-list-2024.png)](https://www.openwall.com/lists/musl/2024/12/31/2)\nthis thread is about busybox `passwd` breaking on a 257 character password. same `\"*\"`, same limit. nobody says \"sshd\"\n\n[openssh-commits · 30 oct 2026 **Address**lists.mindrot.org/pipermail/openssh-commits/2026-October/013271.html ![Image 12: fix fake password salt generation for bcrypt hashes](https://sshhole.com/receipts/openssh-84f8f4666.png)](http://lists.mindrot.org/pipermail/openssh-commits/2026-October/013271.html)\na security review fixes `pick_salt()`. the bug is four lines below it. four days before i found it.\n\nnov 2026\n\n## how i ran into it\n\ni was messing around with openssh, mostly the boring parts where it talks to libc, like the password code. people don't really look at that stuff, they look at the crypto. so i built sshd every way i could think of (glibc, musl, pam, no pam, shadow, no shadow) and threw like 17,600 weird logins at it. weird hashes, broken accounts, passwords way too long\n\noh did i say \"i\"? sorry. i had agent swarms. a lot of them. let's not get into it\n\nevery build agreed on every login. except musl without pam. that one said yes to things it shouldn't\n\ntl;dr\n\n![Image 13: six panel comic: 1980 daemon gets a star; 2012 musl crypt returns star instead of NULL; 2016 openssh borrows bob's salt; 2021 alpine changes root from ! to star, narrator: it did not; 2016 to 2026 a cat sleeps on a server; 2026 me and some agents, 300 A's give uid 0](https://sshhole.com/comic.svg)\n## try it\n\none debian box, one alpine box. type stuff. it all runs right here in your browser, nothing gets sent anywhere\n\nozgun 256 × A 300 × A clear\n\n256\n\n1024\n\n0 bytes\n\ndebian · glibc\n\ncrypt(pw, bob's salt)\n\nalice's field\n\n*\n\nalpine · musl\n\ncrypt(pw, bob's salt)\n\nalice's field\n\n*\n\n## are you affected?\n\n* is your sshd running on **musl**? (alpine, openwrt, buildroot, yocto)\n* is it **not using pam**? alpine's `openssh-server` doesn't by default, or maybe you set `UsePAM no`\n* are **password logins** still on? they are by default\n* is there an account with just `*` as its password? key-only users, ldap users, root on alpine\n* and some _other_ account with a real password?\n* then that `*` account takes any password between 257 and 1024 characters\n\non alpine's official aws and azure images that's the default `alpine` user, and it has passwordless `doas`. so it's root\n\non debian, ubuntu, fedora or anything else with glibc? going through pam? dropbear? openbsd? you're fine\n\n## what now\n\n_you_\n\n# update. openssh 10.6p2 fixes it.\n$ apk upgrade openssh\n\n# can't update yet? turn password logins off.\n$ echo \"PasswordAuthentication no\" > /etc/ssh/sshd_config.d/00-no-passwords.conf\n$ rc-service sshd restart\n\none more thing\n\n## did you get hacked? check.\n\n_root@your-box_\n\nsee a line like that? an account with no password just took a password\n\nif that's the case…\n\ni'm sorry.\n\nyou got hacked.\n\nby an\n\n*sshole\n\nfound by [**ozgun kultekin**](https://ozgun.sh/) at [wakefield](https://wakefield.co/)\n\nwe're hiring. [wakefield.co/careers](https://wakefield.co/careers)","body_html":"\u003ch1 id=\"ss-h-ole\">*ss h ole\u003c/h1>\n\u003cp>so openssh on musl linux (alpine, openwrt, buildroot, yocto, and a lot of the docker images you've pulled) has had a little problem since 2016.\u003c/p>\n\u003cp>accounts that should never take a password at all (root, your key-only deploy user, ldap users, the default user on alpine's aws and azure images) take any password longer than 256 characters.\u003c/p>\n\u003cp>yes, any password.yes.i know.yes.\u003c/p>\n\u003col>\u003cli>1980 the first star\u003c/li>\u003cli>1990s the password check\u003c/li>\u003cli>1990s the fine print\u003c/li>\u003cli>2012 crypt stops saying NULL\u003c/li>\u003cli>2012 the 256-byte cap\u003c/li>\u003cli>2016 bob's salt\u003c/li>\u003cli>2019 the fix for the fix\u003c/li>\u003cli>2024 ten quiet years\u003c/li>\u003cli>2026 how i ran into it\u003c/li>\u003c/ol>\n\u003cp>1980\u003c/p>\n\u003ch2 id=\"the-first-star\">the first star\u003c/h2>\n\u003cp>back in old unix your password hash just sat in \u003ccode>/etc/passwd\u003c/code>, right next to your username. in a file everyone could read.\u003c/p>\n\u003cp>in 1980 bill joy put a \u003ccode>*\u003c/code> there for an account called \u003ccode>daemon\u003c/code>. nobody's supposed to ever log in as it.\u003c/p>\n\u003cp>a \u003ccode>*\u003c/code> isn't a hash, so no password can match it. unix still does this today\u003c/p>\n\u003cp>\u003ca href=\"https://github.com/dspinellis/unix-history-repo/blob/BSD-3/etc/passwd\" rel=\"nofollow ugc noopener\">3bsd · /etc/passwd · 1980 \u003cstrong>Address\u003c/strong>github.com/dspinellis/unix-history-repo/blob/BSD-3/etc/passwd \u003cimg src=\"https://sshhole.com/receipts/3bsd-passwd.png\" alt=\"Image 1: daemon:*:1:1:The devil himself:/:\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/a>\nthe next field is the real name. he wrote "the devil himself"\u003c/p>\n\u003cp>1990s\u003c/p>\n\u003ch2 id=\"how-sshd-checks-your-password\">how sshd checks your password\u003c/h2>\n\u003cp>ok so these days the hash lives in \u003ccode>/etc/shadow\u003c/code> and looks like \u003ccode>$6$abc$k2P9…\u003c/code>. the \u003ccode>$6$\u003c/code> means sha512, \u003ccode>abc\u003c/code> is the salt, the rest is the actual hash\u003c/p>\n\u003cp>you type your password, sshd hashes it with that same salt and checks if it comes out identical. same = you're in. that's it\u003c/p>\n\u003cp>and if the field is just \u003ccode>*\u003c/code>? there's nothing to match. type whatever you want, it's never getting you in\u003c/p>\n\u003cp>1990s\u003c/p>\n\u003ch2 id=\"the-fine-print\">the fine print\u003c/h2>\n\u003cp>one more rule. if \u003ccode>crypt()\u003c/code> can't do its job, it returns NULL. like if the salt asks for some algorithm the system doesn't have, there's nothing to compute, so you get NULL instead of a hash\u003c/p>\n\u003cp>\u003ca href=\"https://pubs.opengroup.org/onlinepubs/7908799/xsh/crypt.html\" rel=\"nofollow ugc noopener\">the single unix spec · crypt() · 1997 \u003cstrong>Address\u003c/strong>pubs.opengroup.org/onlinepubs/7908799/xsh/crypt.html \u003cimg src=\"https://sshhole.com/receipts/posix-crypt.png\" alt=\"Image 2: RETURN VALUE: Upon successful completion, crypt() returns a pointer to the encoded string. Otherwise it returns a null pointer and sets errno to indicate the error.\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/a>\npretty clear.\u003c/p>\n\u003cp>except a lot of programs never check for NULL. they just compare whatever \u003ccode>crypt()\u003c/code> gives back with the stored field, hit the NULL, and crash\u003c/p>\n\u003cp>2012\u003c/p>\n\u003ch2 id=\"crypt-stops-saying-null\">crypt stops saying NULL\u003c/h2>\n\u003cp>so musl (the libc under alpine) goes ok fine, \u003ccode>crypt()\u003c/code> just won't return NULL anymore. if it fails, it returns a single character instead. that character can never match a real password, so programs don't crash, they just see a wrong password\u003c/p>\n\u003cp>now guess which character they picked for that\u003c/p>\n\u003cp>"?"\u003c/p>\n\u003cp>yep. the star. again.\u003c/p>\n\u003cp>\u003ca href=\"https://git.musl-libc.org/cgit/musl/commit/?id=b3c4cc121f70faea45389fe7ddc1127ed5cbd8bb\" rel=\"nofollow ugc noopener\">musl · b3c4cc12 · aug 2012 \u003cstrong>Address\u003c/strong>git.musl-libc.org/cgit/musl/commit/?id=b3c4cc12 \u003cimg src=\"https://sshhole.com/receipts/musl-b3c4cc12.png\" alt=\"Image 3: make crypt return an unmatchable hash rather than NULL on failure. always "succeeding" but giving an unmatchable hash is reportedly a better behavior than failing on error.\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/a>\n"reportedly."\u003c/p>\n\u003cp>\u003ca href=\"https://git.musl-libc.org/cgit/musl/commit/?id=b3c4cc121f70faea45389fe7ddc1127ed5cbd8bb\" rel=\"nofollow ugc noopener\">musl · b3c4cc12 · the diff \u003cstrong>Address\u003c/strong>git.musl-libc.org/cgit/musl/commit/?id=b3c4cc12 \u003cimg src=\"https://sshhole.com/receipts/musl-b3c4cc12-diff.png\" alt=\"Image 4: diff of crypt_des.c: removed the comment 'Should not happen.' and 'return NULL;', added: return (setting[0]=='*') ? "x" : "*";\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/a>\n"should not happen" gone, NULL gone, \u003ccode>"*"\u003c/code> in\u003c/p>\n\u003cp>2012\u003c/p>\n\u003ch2 id=\"three-weeks-later\">three weeks later\u003c/h2>\n\u003cp>then musl adds sha512 crypt. the thing is, sha512crypt gets slower the longer the password is, so someone could send one giant password and keep your server busy for a long time. so musl just caps it at 256 bytes and refuses anything longer\u003c/p>\n\u003cp>\u003ca href=\"https://git.musl-libc.org/cgit/musl/commit/?id=88bf5a8a8d7d796f63cca8589f4de67aa8345f1a\" rel=\"nofollow ugc noopener\">musl · 88bf5a8a · aug 29 2012 \u003cstrong>Address\u003c/strong>git.musl-libc.org/cgit/musl/commit/?id=88bf5a8a \u003cimg src=\"https://sshhole.com/receipts/musl-88bf5a8a.png\" alt=\"Image 5: add sha256/sha512 crypt. Rich Felker, 2012-08-29.\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/a>\ntwenty days after the "*" commit btw\u003c/p>\n\u003cp>\u003ca href=\"https://git.musl-libc.org/cgit/musl/tree/src/misc/crypt_sha512.c?id=88bf5a8a8d7d796f63cca8589f4de67aa8345f1a#n189\" rel=\"nofollow ugc noopener\">musl · crypt_sha512.c @ 88bf5a8a \u003cstrong>Address\u003c/strong>git.musl-libc.org/cgit/musl/tree/src/misc/crypt_sha512.c?id=88bf5a8a \u003cimg src=\"https://sshhole.com/receipts/musl-keymax.png\" alt=\"Image 6: key limit is not part of the original design, added for DoS protection. #define KEY_MAX 256. if (i > KEY_MAX) return 0;\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/a>\nso past 256 bytes crypt fails. and when crypt fails… it says \u003ccode>"*"\u003c/code>.\u003c/p>\n\u003cp>\u003ca href=\"https://git.musl-libc.org/cgit/musl/tree/src/crypt/crypt_sha512.c#n8\" rel=\"nofollow ugc noopener\">musl · crypt_sha512.c \u003cstrong>Address\u003c/strong>git.musl-libc.org/cgit/musl/tree/src/crypt/crypt_sha512.c \u003cimg src=\"https://sshhole.com/receipts/musl-sha512-header.png\" alt=\"Image 7: on error "*" is returned.\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/a>\nliterally in the comment the whole time\u003c/p>\n\u003cp>2016\u003c/p>\n\u003ch2 id=\"sshd-borrows-bob-s-salt\">sshd borrows bob's salt\u003c/h2>\n\u003cp>CVE-2016-6210. ask sshd about a user that doesn't exist and it says no instantly, cause there's nothing to hash. real users take a few ms longer. so just time it and you know who exists\u003c/p>\n\u003cp>the fix is kinda funny. no real hash to check? sshd grabs some other account's salt and hashes your password anyway, just to waste the same amount of time. still a no, just a slower no\u003c/p>\n\u003cp>\u003ca href=\"http://lists.mindrot.org/pipermail/openssh-commits/2016-July/005428.html\" rel=\"nofollow ugc noopener\">openssh-commits · jul 2016 \u003cstrong>Address\u003c/strong>lists.mindrot.org/pipermail/openssh-commits/2016-July/005428.html \u003cimg src=\"https://sshhole.com/receipts/openssh-9286875a7.png\" alt=\"Image 8: Determine appropriate salt for invalid users.\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/a>\n"for invalid users." and also, it turns out, real users with a \u003ccode>*\u003c/code>.\u003c/p>\n\u003cp>2019 → 2022\u003c/p>\n\u003ch2 id=\"the-fix-for-the-fix\">the fix for the fix\u003c/h2>\n\u003cp>\u003cstrong>2019.\u003c/strong> turns out alpine's docker images had no root password. at all. CVE-2019-5021. alpine fixes it by locking root with \u003ccode>!\u003c/code>\u003c/p>\n\u003cp>but without pam, \u003ccode>!\u003c/code> also kills ssh keys. and cloud images log in with keys.\u003c/p>\n\u003cp>\u003cstrong>2022.\u003c/strong> alpine 3.16 switches root to \u003ccode>*\u003c/code>. still locked, keys work again\u003c/p>\n\u003cp>\u003ca href=\"https://gitlab.alpinelinux.org/alpine/aports/-/commit/fbe926afc76de76e07d078f266badc4144dde8e3\" rel=\"nofollow ugc noopener\">alpine aports · fbe926af · shipped in 3.16, 2022 \u003cstrong>Address\u003c/strong>gitlab.alpinelinux.org/alpine/aports/-/commit/fbe926af.patch \u003cimg src=\"https://sshhole.com/receipts/alpine-fbe926af.png\" alt=\"Image 9: this still forbids password login but allows logins via ssh keys with pam disabled. # make sure root login is disabled. root:! becomes root:*\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/a>\nnarrator: it did not.\u003c/p>\n\u003cp>2016 → 2026\u003c/p>\n\u003ch2 id=\"ten-quiet-years\">ten quiet years\u003c/h2>\n\u003cp>why did nobody notice? well, maybe someone did. maybe someone pasted the wrong thing into a password prompt, half a slack message or a whole ssh key, and it just let them in. you've never pasted the wrong thing into a password prompt?? amazing. a fresh box with no passwords set isn't affected. a \u003ccode>*\u003c/code> in shadow needs a wrong try first. openssh tests on openbsd and glibc, musl doesn't test sshd, and most distros go through pam, which never even calls crypt for a \u003ccode>*\u003c/code>.\u003c/p>\n\u003cp>so as far as anyone knows, nobody noticed. as far as anyone knows.\u003c/p>\n\u003cp>some people got really close though\u003c/p>\n\u003cp>\u003ca href=\"https://bugs.debian.org/714219\" rel=\"nofollow ugc noopener\">libc-alpha · debian #714219 · 2013 \u003cstrong>Address\u003c/strong>sourceware.org/legacy-ml/libc-alpha/2013-07/msg00046.html \u003cimg src=\"https://sshhole.com/receipts/libc-alpha-2013.png\" alt=\"Image 10: The scheme of returning * or x, which are never valid matches, comes from dalias from musl, and I think it is the best compromise/solution.\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/a>\na debian dev asks glibc to copy musl's \u003ccode>"*"\u003c/code>. six years later debian moves to libxcrypt, which says \u003ccode>"*0"\u003c/code>, and closes the bug. one character away.\u003c/p>\n\u003cp>\u003ca href=\"https://www.openwall.com/lists/musl/2024/12/31/2\" rel=\"nofollow ugc noopener\">musl mailing list · dec 2024 \u003cstrong>Address\u003c/strong>openwall.com/lists/musl/2024/12/31/2 \u003cimg src=\"https://sshhole.com/receipts/musl-list-2024.png\" alt=\"Image 11: Sure there's no reason it couldn't have been 257 or 300 or whatever, but either way you'd get things like this when software has bugs in handling the condition.\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/a>\nthis thread is about busybox \u003ccode>passwd\u003c/code> breaking on a 257 character password. same \u003ccode>"*"\u003c/code>, same limit. nobody says "sshd"\u003c/p>\n\u003cp>\u003ca href=\"http://lists.mindrot.org/pipermail/openssh-commits/2026-October/013271.html\" rel=\"nofollow ugc noopener\">openssh-commits · 30 oct 2026 \u003cstrong>Address\u003c/strong>lists.mindrot.org/pipermail/openssh-commits/2026-October/013271.html \u003cimg src=\"https://sshhole.com/receipts/openssh-84f8f4666.png\" alt=\"Image 12: fix fake password salt generation for bcrypt hashes\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/a>\na security review fixes \u003ccode>pick_salt()\u003c/code>. the bug is four lines below it. four days before i found it.\u003c/p>\n\u003cp>nov 2026\u003c/p>\n\u003ch2 id=\"how-i-ran-into-it\">how i ran into it\u003c/h2>\n\u003cp>i was messing around with openssh, mostly the boring parts where it talks to libc, like the password code. people don't really look at that stuff, they look at the crypto. so i built sshd every way i could think of (glibc, musl, pam, no pam, shadow, no shadow) and threw like 17,600 weird logins at it. weird hashes, broken accounts, passwords way too long\u003c/p>\n\u003cp>oh did i say "i"? sorry. i had agent swarms. a lot of them. let's not get into it\u003c/p>\n\u003cp>every build agreed on every login. except musl without pam. that one said yes to things it shouldn't\u003c/p>\n\u003cp>tl;dr\u003c/p>\n\u003cfigure>\u003cimg src=\"https://sshhole.com/comic.svg\" alt=\"Image 13: six panel comic: 1980 daemon gets a star; 2012 musl crypt returns star instead of NULL; 2016 openssh borrows bob's salt; 2021 alpine changes root from ! to star, narrator: it did not; 2016 to 2026 a cat sleeps on a server; 2026 me and some agents, 300 A's give uid 0\" loading=\"lazy\" decoding=\"async\" referrerpolicy=\"no-referrer\" />\u003c/figure>\n\u003ch2 id=\"try-it\">try it\u003c/h2>\n\u003cp>one debian box, one alpine box. type stuff. it all runs right here in your browser, nothing gets sent anywhere\u003c/p>\n\u003cp>ozgun 256 × A 300 × A clear\u003c/p>\n\u003cp>256\u003c/p>\n\u003cp>1024\u003c/p>\n\u003cp>0 bytes\u003c/p>\n\u003cp>debian · glibc\u003c/p>\n\u003cp>crypt(pw, bob's salt)\u003c/p>\n\u003cp>alice's field\u003c/p>\n\u003cp>*\u003c/p>\n\u003cp>alpine · musl\u003c/p>\n\u003cp>crypt(pw, bob's salt)\u003c/p>\n\u003cp>alice's field\u003c/p>\n\u003cp>*\u003c/p>\n\u003ch2 id=\"are-you-affected\">are you affected?\u003c/h2>\n\u003cul>\u003cli>is your sshd running on \u003cstrong>musl\u003c/strong>? (alpine, openwrt, buildroot, yocto)\u003c/li>\u003cli>is it \u003cstrong>not using pam\u003c/strong>? alpine's \u003ccode>openssh-server\u003c/code> doesn't by default, or maybe you set \u003ccode>UsePAM no\u003c/code>\u003c/li>\u003cli>are \u003cstrong>password logins\u003c/strong> still on? they are by default\u003c/li>\u003cli>is there an account with just \u003ccode>*\u003c/code> as its password? key-only users, ldap users, root on alpine\u003c/li>\u003cli>and some \u003cem>other\u003c/em> account with a real password?\u003c/li>\u003cli>then that \u003ccode>*\u003c/code> account takes any password between 257 and 1024 characters\u003c/li>\u003c/ul>\n\u003cp>on alpine's official aws and azure images that's the default \u003ccode>alpine\u003c/code> user, and it has passwordless \u003ccode>doas\u003c/code>. so it's root\u003c/p>\n\u003cp>on debian, ubuntu, fedora or anything else with glibc? going through pam? dropbear? openbsd? you're fine\u003c/p>\n\u003ch2 id=\"what-now\">what now\u003c/h2>\n\u003cp>\u003cem>you\u003c/em>\u003c/p>\n\u003ch1 id=\"update-openssh-10-6p2-fixes-it\">update. openssh 10.6p2 fixes it.\u003c/h1>\n\u003cp>$ apk upgrade openssh\u003c/p>\n\u003ch1 id=\"can-t-update-yet-turn-password-logins-off\">can't update yet? turn password logins off.\u003c/h1>\n\u003cp>$ echo "PasswordAuthentication no" > /etc/ssh/sshd_config.d/00-no-passwords.conf\n$ rc-service sshd restart\u003c/p>\n\u003cp>one more thing\u003c/p>\n\u003ch2 id=\"did-you-get-hacked-check\">did you get hacked? check.\u003c/h2>\n\u003cp>\u003cem>root@your-box\u003c/em>\u003c/p>\n\u003cp>see a line like that? an account with no password just took a password\u003c/p>\n\u003cp>if that's the case…\u003c/p>\n\u003cp>i'm sorry.\u003c/p>\n\u003cp>you got hacked.\u003c/p>\n\u003cp>by an\u003c/p>\n\u003cp>*sshole\u003c/p>\n\u003cp>found by \u003ca href=\"https://ozgun.sh/\" rel=\"nofollow ugc noopener\">\u003cstrong>ozgun kultekin\u003c/strong>\u003c/a> at \u003ca href=\"https://wakefield.co/\" rel=\"nofollow ugc noopener\">wakefield\u003c/a>\u003c/p>\n\u003cp>we're hiring. \u003ca href=\"https://wakefield.co/careers\" rel=\"nofollow ugc noopener\">wakefield.co/careers\u003c/a>\u003c/p>","headings":[{"level":1,"text":"*ss h ole","id":"ss-h-ole"},{"level":2,"text":"the first star","id":"the-first-star"},{"level":2,"text":"how sshd checks your password","id":"how-sshd-checks-your-password"},{"level":2,"text":"the fine print","id":"the-fine-print"},{"level":2,"text":"crypt stops saying NULL","id":"crypt-stops-saying-null"},{"level":2,"text":"three weeks later","id":"three-weeks-later"},{"level":2,"text":"sshd borrows bob's salt","id":"sshd-borrows-bob-s-salt"},{"level":2,"text":"the fix for the fix","id":"the-fix-for-the-fix"},{"level":2,"text":"ten quiet years","id":"ten-quiet-years"},{"level":2,"text":"how i ran into it","id":"how-i-ran-into-it"},{"level":2,"text":"try it","id":"try-it"},{"level":2,"text":"are you affected?","id":"are-you-affected"},{"level":2,"text":"what now","id":"what-now"},{"level":1,"text":"update. openssh 10.6p2 fixes it.","id":"update-openssh-10-6p2-fixes-it"},{"level":1,"text":"can't update yet? turn password logins off.","id":"can-t-update-yet-turn-password-logins-off"},{"level":2,"text":"did you get hacked? check.","id":"did-you-get-hacked-check"}]}}